All posts by Ed Tittel

Full-time freelance writer, researcher and occasional expert witness, I specialize in Windows operating systems, information security, markup languages, and Web development tools and environments. I blog for numerous Websites, still write (or revise) the occasional book, and write lots of articles, white papers, tech briefs, and so forth.

Iphone SMS Failure 2FA Cascade

Recently, my iPhone 12 developed a particularly inconvenient communications problem. SMS messages from multiple online services simply stopped showing up. Ordinary phone use looked normal, but two-factor authentication (2FA) did not. When a site wanted to send me a one-time code by SMS, that code often went MIA. That turned routine account maintenance into an obstacle course, and provoked an iPhone SMS failure 2FA cascade. Let me explain…

Finding & Fixing Iphone SMS Failure 2FA Cascade

After doing the usual checking, I called Spectrum, my wireless provider. That turned into a surprisingly positive support encounter. The network support representative worked the carrier side while I worked on the iPhone.

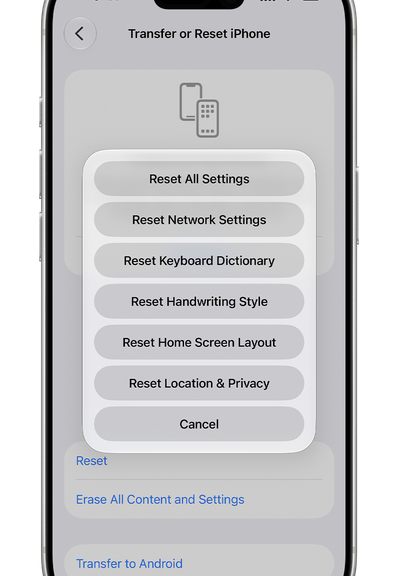
The prescription was straightforward. I reset the iPhone’s network settings (item 2 in lead-in graphic) while Spectrum reset and resynchronized things on its end. Apple’s documentation confirms that Reset Network Settings removes saved network settings, including Wi-Fi networks and passwords, cellular settings, and VPN and APN settings. It does not amount to erasing the phone.

Once both sides had been refreshed, SMS delivery returned to normal. Verification codes started arriving again. That’s the outcome that matters most. Whatever had become unsynchronized between handset and network was apparently cleared by rebuilding the relationship from both ends. I’m not sure what caused this, but it started happening aftera recent iOS update (26.7.2) on October 26.

Next Comes Account Cleanup…Sigh

Restoring SMS did not magically undo everything that happened while those messages were missing. Now I’m going through affected online accounts to make sure authentication, billing, and other notices are behaving normally.

That exercise immediately produced an unwelcome surprise at Box.com. I discovered a $500-plus invoice for online file-exchange service. The subscription covers three seats even though I’m using none (and don’t really need the subscription anymore).

Getting Outside the Box

I started investigating how to reduce that bill. Box’s published support information says paid accounts subject to its seat-reduction policy have a three-seat minimum. It also says seat decreases can be processed only at the end of the account term. Removing users by itself does not reduce subscription charges.

Refund language isn’t particularly comforting, either. Box says services are prepaid and generally non-refundable, including renewed accounts. Its support material does allow eligible customers to request a refund for a renewal charge through Billing, but that is a request, not a promise.

Those rules may make contractual sense from Box’s point of view. From where I sit, though, paying more than $500 for three seats when I’m using none makes little sense. If I cannot unwind a freshly discovered renewal, this may end a very long business relationship.

A Bigger Lesson For Yours Truly

The episode started as an iPhone messaging problem and turned into an account audit. That’s probably a useful takeaway. When SMS-based 2FA stops working across multiple unrelated services, don’t assume every account has suddenly broken. The common dependency may be the phone or carrier connection.

In my case, resetting network settings while Spectrum refreshed its side fixed my immediate SMS problem. The follow-on work is less pleasant, but perhaps equally valuable. I’m now checking the accounts that depend on those messages, fixing what needs fixing, and reconsidering services whose billing arrangements fall outside my pain threshold. Sometimes a communications failure tells you more than you expected to learn. Here in Windows-World, that means “It’s Tuesday.”

Facebooklinkedin
Facebooklinkedin

Repair Install Requires Local Logins for Working RDP

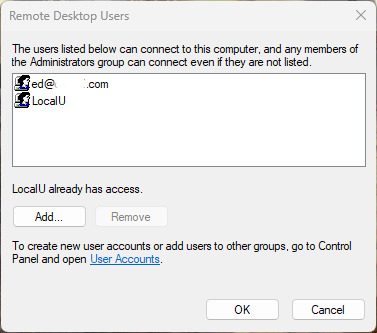
Here’s an interesting Windows 11 gotcha I ran into after a recent repair install on RyzenOfc. Remote Desktop worked perfectly with a local administrator account, but my usual Microsoft account refused a known-good password. The eventual fix was surprisingly simple: I had to log into RyzenOfc locally with that Microsoft account and its password once. Hence this post’s title: repair install requires local logins for working RDP.

That local login triggered the familiar “Setting a few things up…” sequence. After Windows finished its abbreviated OOBE-style setup, the same Microsoft account immediately worked for RDP from Flo6. Along the way, PowerShell provided some useful clues about what had survived the repair install and what had not.

Why Repair Install Requires Local Logins

From the get-go, I could RDP from Flo6 into RyzenOfc using the local administrator account LocalU. That eliminated a long list of suspects. The network path worked, Remote Desktop was enabled, and the target system was accepting RDP connections. Indeed, the failure was specific to my Microsoft account.

Windows returned the wonderfully nonspecific message “Your credentials did not work.” I knew the password was correct, so I started by examining the accounts RyzenOfc knew about.

PowerShell Exposes 2 MSAs

This command listed the local account records and their origins:

Get-CimInstance Win32_UserAccount -Filter "LocalAccount=True" |
Select-Object Name, Caption, SID, Disabled

The interesting entries were ed and etitt. Both showed up as MicrosoftAccount identities (aka MSAs). I already knew etitt belonged to an old, obsolete  Microsoft account. That made ed, with SID ending in -1002, the account of interest. In fact, that’s my current go-to user account.

Next I checked RDP and administrator group membership:

Get-LocalGroupMember -Group "Remote Desktop Users"

Get-LocalGroupMember -Group “Administrators”

That produced another important clue. RYZENOFC\ed was already a member of Remote Desktop Users. RYZENOFC\etitt and LocalU were administrators. Thus the ed account did not lack RDP permission. Adding it to Administrators would have treated the symptom as a permissions problem when the evidence pointed elsewhere.

Missing Profile = Smoking Gun

I then looked at the account objects more closely:

Get-LocalUser |
Select-Object Name, SID, PrincipalSource, Enabled, LastLogon

Both ed and etitt were enabled and identified as MicrosoftAccount principals. But a query for their Windows profiles changed the picture:

Get-CimInstance Win32_UserProfile |

Where-Object SID -in @(
‘S-1-5-21-144170778-2336474949-3120614169-1001’,
‘S-1-5-21-144170778-2336474949-3120614169-1002’) |
Select-Object LocalPath, SID, Loaded, LastUseTime

Only the old etitt identity appeared, mapped to C:\Users\etitt. There was no Win32_UserProfile entry for ed. RyzenOfc knew that ed existed and even knew it was allowed to use Remote Desktop, but Windows had not yet initialized that user environment following the repair install.

Local Login Closes the Loop

That observation reminded me of something important: I had not logged into RyzenOfc with the ed@edtittel.com/password combination since performing a repair install a couple of weeks earlier. I had been relying on Windows Hello rather than forcing a conventional password login.

So I did exactly that at RyzenOfc. I selected the ed account, chose password sign-in, and supplied the known-good Microsoft account password. Windows responded with “Setting a few things up…” and went through the familiar first-login setup sequence.

That message explained a lot. The Microsoft account registration had survived, but Windows still needed to finish initializing the user’s post-repair environment. The password-based sign-in also gave Windows a fresh interactive authentication event for that Microsoft account on the target PC.

THEN, RDP Gets to Workin’

Windows Hello and a Microsoft account password are related to the same identity, but they are not interchangeable credentials. A Hello PIN is tied to the device and protected through Windows Hello mechanisms. An ordinary RDP connection using a Microsoft account password needs the target Windows installation to be able to validate that password-based identity.

Microsoft documentation describes Windows Hello as using cryptographic keys, while Microsoft community reports describe RDP failures after setup when password-based sign-in has not been established locally. Those reports also describe a successful local password login as restoring RDP password authentication.

That matches my RyzenOfc experience. Once the local login completed account and profile setup, I returned to Flo6 and connected using the ed Microsoft account. This time RDP accepted the same password it had rejected before.

Here Cometh the Lesson

The practical takeaway is straightforward. After a Windows repair install, don’t assume a preserved Microsoft account is fully ready for every authentication path just because Windows still lists it.

If RDP works with a local administrator but rejects a known-good Microsoft account password, check the account source, Remote Desktop Users membership, and Win32_UserProfile state before changing security policy. If the Microsoft-account profile has not been initialized, perform one local interactive login using the actual password rather than the PIN.

In my case, that little “Setting a few things up…” message told the story. Windows was finishing work the repair install had left pending. Once it completed, RDP was back in business. Here in Windows-World, I count that as a win!

Facebooklinkedin
Facebooklinkedin

Quick WLAN Profile Cleanup

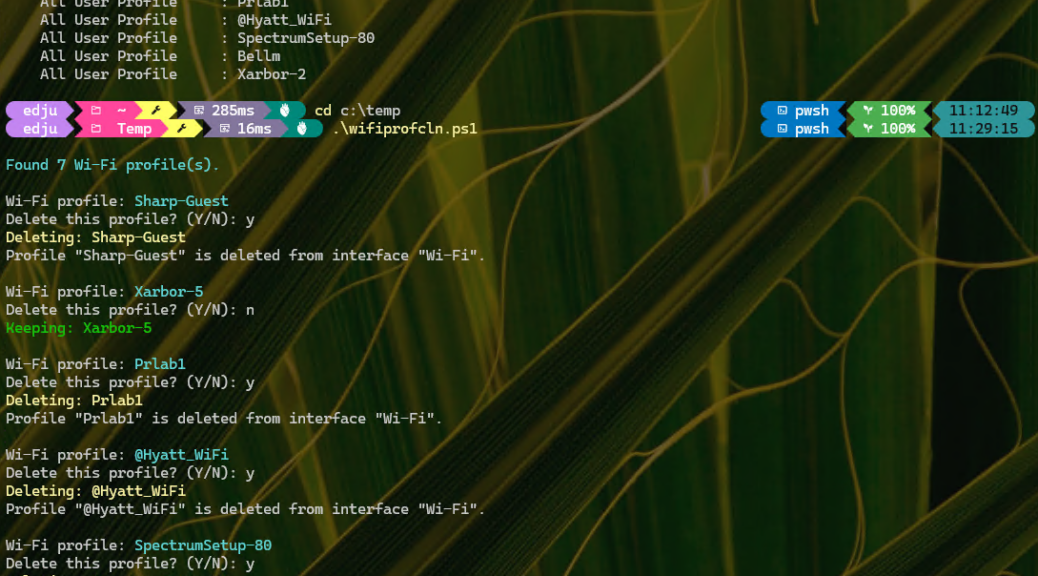
I’ve known for a long, long time that the netsh wlan show profiles command lists known Wi-Fi networks on suitably equipped Windows PCs. Until now, I’ve periodically used that command to check how many I’ve got and how many I don’t really need. Now, thanks to Copilot’s “script on demand” abilities, I’ve got a script that walks me through the list. It offers a quick WLAN profile cleanup, so I can keep the ones I use, and deep-six the ones I don’t.

PowerShell For Quick WLAN Profile Cleanup

The screencap starts with the list of 7 known wi-fi networks on the Lenovo ThinkPad X380 Yoga. Of the 7 networks shown, I only need 2 of them.

The script (named wifiprofcln.ps1) walks through all known WLAN profiles for Wi-Fi networks, then asks whether to keep or delete each one. As you can see in the screencap, I deleted 5 and kept 2 of the 7 I started out with. Some were from hotels, others from offices, others from my cellphone provider’s hotspot network.

The Real Beauty of On-Demand Scripting

This is just a simple bit of throwaway PowerShell. The script is 40 lines long. It took Copilot less time to build it than it took me to tell it what I wanted the script to do. At one time, I would’ve been inclined to deliver this info as a recipe with the proper way to structure commands and let readers DIY their way through it. Now, I can put together and share a quickie one-off tool in minutes.

Say what you want about the evils of AI, the perils of hallucination or misalignment, or even existential threats. This kind of simple, straightforward use is easy, fast and pretty darn useful. Within scope and with a tight focus, it’s a complete boon to getting things done here in Windows-World. Use it carefully, to be sure, but use it you must!

Facebooklinkedin
Facebooklinkedin

More Discord Follies: Unactivated Download

Sometimes an update problem gets more interesting after the obvious fix succeeds. That just happened to me with Discord on Windows. WinGet insisted version 1.0.9267 was available, while my PC remained on 1.0.9266. Even stranger, forcing the upgrade did not change the reported installed version.

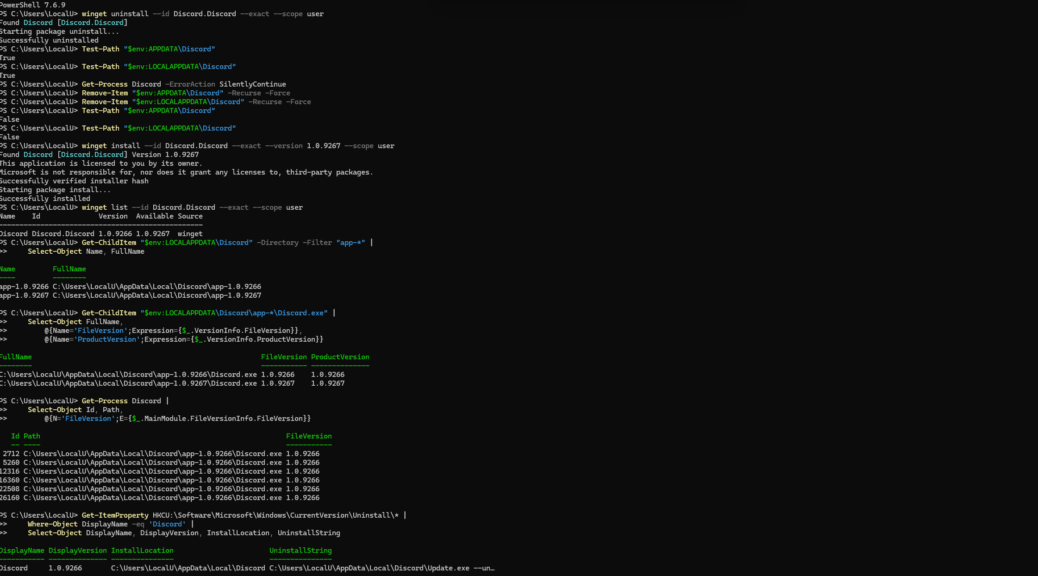
I tried WinGet, UniGetUI and Discord’s in-app updater. Nothing moved the needle. Eventually I performed a clean uninstall and reinstall. That exercise exposed what was really happening: version 1.0.9267 had downloaded, but Discord was still running 1.0.9266. That’s how I found myself engaged in more Discord Follies: unactivated download is present, but inert. WTF?

Unpacking More Discord Follies: Unactivated Download

The basic inventory command showed the mismatch clearly:
winget list --id Discord.Discord --exact --scope user

It reported 1.0.9266 installed and 1.0.9267 available. Discord was installed at user scope, which also produced an instructive side trip. An elevated WinGet session refused to uninstall the per-user package. Switching to a normal Windows Terminal session fixed that.

winget uninstall --id Discord.Discord --exact --scope user

After the uninstall succeeded, I checked for leftovers:

Test-Path "$env:APPDATA\Discord"
Test-Path "$env:LOCALAPPDATA\Discord"

Both returned True. With no Discord processes still running, I removed those directories and verified that both paths returned False. That gave me the clean slate I wanted.

The Clean Install Surprise!

Next came an explicit installation of the supposedly newer release:

winget install --id Discord.Discord --exact --version 1.0.9267 --scope user

WinGet found 1.0.9267, verified its installer hash and reported a successful installation. Yet another winget list still showed 1.0.9266 installed, with 1.0.9267 available. At first glance, that looked impossible.

The file system told a better story. I enumerated Discord’s version directories:

Get-ChildItem "$env:LOCALAPPDATA\Discord" -Directory -Filter "app-*" | Select-Object Name, FullName

There were two of them: app-1.0.9266 and app-1.0.9267. Checking the Discord.exe files confirmed that each directory contained the version its name advertised. Again: WTF?

Installed Is Not Activated, Apparently

The decisive check was to examine the running processes instead of trusting package inventory alone:

Get-Process Discord | Select-Object Id, Path,
@{N='FileVersion';E={$_.MainModule.FileVersionInfo.FileVersion}}

Every running Discord process came from app-1.0.9266. I then checked the per-user uninstall registration:

Get-ItemProperty HKCU:\Software\Microsoft\Windows\CurrentVersion\Uninstall\* |
Where-Object DisplayName -eq 'Discord' |
Select-Object DisplayName, DisplayVersion, InstallLocation, UninstallString

Windows likewise registered Discord as version 1.0.9266. In other words, WinGet was not hallucinating. Version 1.0.9267 really existed on disk, but 1.0.9266 remained the registered and active release.

The Nub of This Discord Folly Is…

Discord’s current generic stable update manifest identifies 1.0.9267 as the host version. I also found installation-specific manifest results that still identify 1.0.9266. That makes staged update selection a plausible explanation for this split state, though the local evidence alone doesn’t completely illuminate  Discord’s rollout policy.

Here, the important lesson is more general. When an updater says success but inventory disagrees, inspect three layers: package registration, files on disk and the executable that’s actually running. Those views might disagree: here they did so spectacularly.

For now, I’m leaving both Discord directories alone. Manually deleting the active release or rewriting its registration would create more, not less

Discord’s current generic stable update manifest identifies 1.0.9267 as the host version. We also found installation-specific manifest results that still identify 1.0.9266. That makes staged update selection a plausible explanation for the split state, although the local evidence alone cannot prove Discord’s rollout policy.

The important lesson is more general. When an updater says success but inventory disagrees, inspect three layers: package registration, files on disk and the executable actually running. Those views can disagree, and here they did spectacularly.

For now, I am leaving both Discord directories alone. Manually deleting the active release or rewriting its registration would create more, not less uncertainty. Here in Windows-World, sometimes the best troubleshooting means knowing exactly why you should stop troubleshooting. I’m done for now, and will wait to see what Discord does next. Sigh.

Further Reading

Discord stable Windows x64 update manifest

Discord Support, Windows Corrupt Installation

Facebooklinkedin
Facebooklinkedin

Checking Hotfix Can Beat Package Check

After reading about KB5127936 and its Cloud Rebuild facility recently, I wondered how many of my production level PCs already sported this Preview CU. So I asked Copilot to craft me some PowerShell to check. Along the way, I learned that: (a) some methods are better than others, and (b) that there are many ways to request such information. It’s also how I learned that checking hofix can beat package check info, depending on what you need.

My first query looked perfectly reasonable:
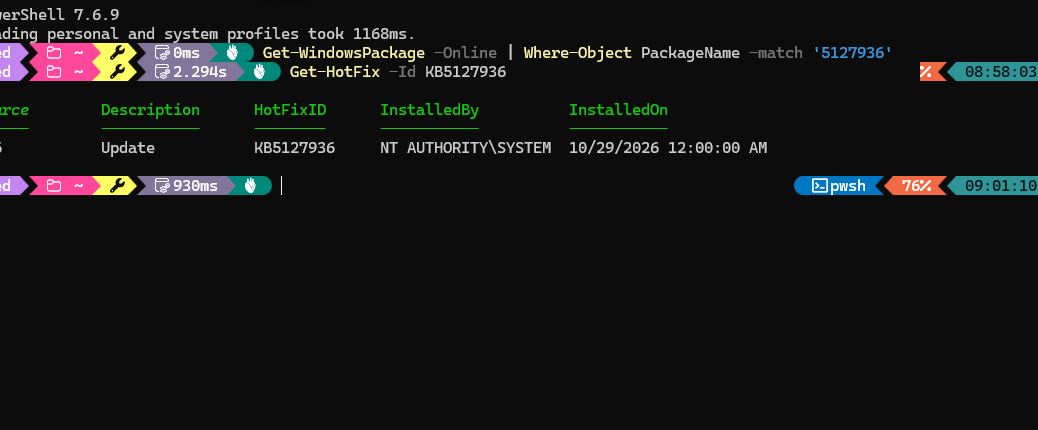
Get-WindowsPackage -Online | Where-Object PackageName -match '5127936'
Alas, that request returned no output. Such a result could tempt an administrator to conclude that the update was absent. Here, that conclusion would be wrong.

Why Checking Hofix Can Beat Package Check

Turns out the afore-cited PowerShell command (which uses DISM under the hood) assumes that the string  “KB5127936” appears in the package metadata. It does not, as it turns out.

However, this simpler command
Get-HotFix -Id KB5127936
produces a direct hit. You can see the outcomes of both commands in the lead-in screencap. After Get-Hotfix, P16 reported KB5127936 as Update, installed by NT AUTHORITY\SYSTEM on October 29, 2026. For the question I was asking, that was exactly the information I needed.

Why the difference? Microsoft documents Get-HotFix as a cmdlet for retrieving installed hotfixes. It uses  Win32_QuickFixEngineering WMI class, whose -Id parameter accepts a hotfix ID. Microsoft even provides an example specifically for verifying whether an update is installed.

In other words, if I start with a KB number, Get-HotFix gives me a KB-oriented lookup. Good stuff!

Get-WindowsPackage Asks Something Different

Get-WindowsPackage is not broken, nor did DISM somehow miss the operating system update. Microsoft describes this cmdlet as a way to obtain information about packages in a Windows image. With -Online, that targets the running Windows installation.

The distinction matters because PackageName is the name of a servicing package inside the image. It is not promised to be the public KB identifier with which its labeled. Microsoft also notes that Get-WindowsPackage cannot provide detailed package information for .msu files, only .cab files. And KB5127936 arrives in .msu form.

Thus my pipeline was really asking, “Does any returned package name contain the characters 5127936?” The empty result answered that narrow question. It did not establish that KB5127936 was missing. And that’s because the package data omits that string. Sigh.

Match the Cmdlet to the Question

This suggests a useful rule of thumb. When somebody hands you a KB number and asks whether that update is installed, try Get-HotFix first:  Get-HotFix -Id KB5127936

For scripts, I like a quiet Boolean-style test:
if (Get-HotFix -Id KB5127936 -ErrorAction SilentlyContinue) { 'INSTALLED' } else { 'NOT FOUND BY GET-HOTFIX' }
That wording is deliberately cautious. Get-HotFix is not a universal inventory of everything Windows Update has ever installed, either. Microsoft defines its scope through QuickFixEngineering. Absence from that view should trigger another check, not a final verdict.

Package Checks Retain Their Value

When I am servicing an online or mounted Windows image, inspecting package identities, or working with CAB-based packages, Get-WindowsPackage remains the right tool. It answers a package-servicing question rather than a KB-history question.

That P16 session reinforced an old Windows lesson: command output only makes sense in the context of the question asked. Here, Get-WindowsPackage told me there was no package name matching my KB string. Get-HotFix told me the update associated with that KB was installed.

Sometimes the simpler check really is the better check. On P16, it certainly was. Here in Windows-World simple is not only faster and easier; it’s a minor but useful labor-saving device!

Further Reading

Microsoft Learn: Get-HotFix (Microsoft.PowerShell.Management)

Microsoft Learn: Get-WindowsPackage (Dism)

Facebooklinkedin
Facebooklinkedin

Revoking P16 CA-2011 Breaks Secure Boot Stalemate

For several days, my Lenovo ThinkPad P16 seemed stuck halfway through Microsoft’s Secure Boot certificate transition. The new 2023 certificates were present, but the Secure-Boot-Update task would not finish the job. Then I revoked the old Microsoft Windows Production PCA 2011 certificate. Finally, it looks like revoking P16 CA-2011 breaks Secure Boot stalemate!

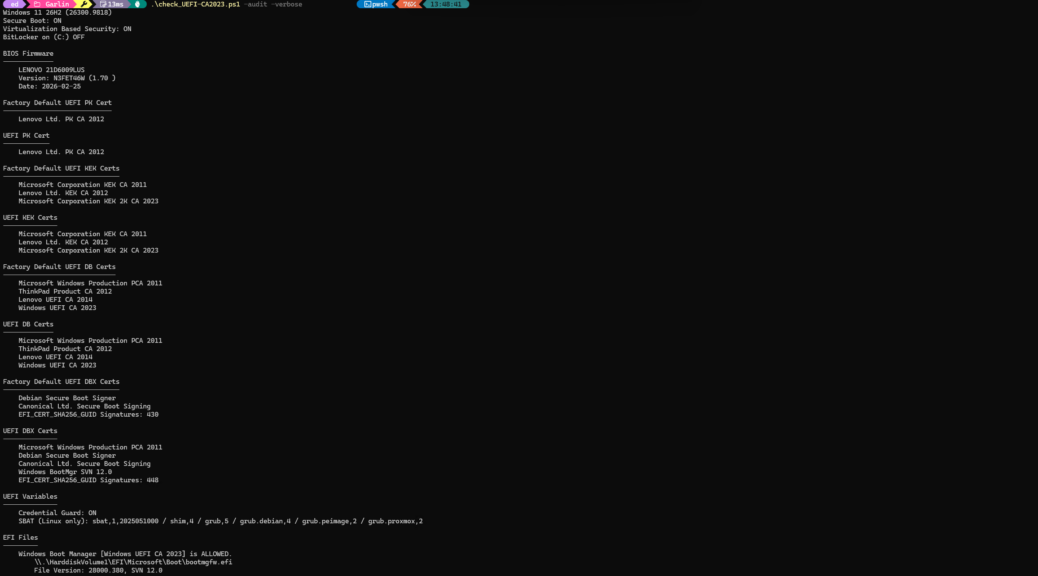
The resulting Garlin check_UEFI-CA2023 audit is the kind of output Windows admins like to see, including yours truly. Every check passes. The Windows UEFI CA 2023 trust chain is active, the newer Boot Manager is in use, and the old PCA 2011 path is revoked.

What changed, and why did revocation apparently matter? That question is worth examining because this 2011-to-2023 transition is becoming increasingly important for Windows PCs.

P16 Breaks Secure Boot Stalemate

Before the final change, this P16 was not exactly broken. Secure Boot was on. Windows booted normally. The 2023 certificates had made their way into the firmware databases. Yet the overall migration remained incomplete.

Repeated efforts to trigger the Microsoft Secure-Boot-Update scheduled task did not transition to the expected state. The task sat at Ready, and Garlin’s checks continued to show that more work remained.

That distinction is useful. A system can remain operational while sitting between the old and new Secure Boot states. Seeing a scheduled task at Ready also does not prove that the complete certificate transition has occurred.

Microsoft Makes It a Staged Transition

Microsoft’s documentation helps explain why. Moving from the 2011 Secure Boot certificates to their 2023 replacements involves more than dropping a certificate into firmware. Microsoft says the change includes new Secure Boot certificates and a Windows Boot Manager signed by the updated trust. All those pieces work together as an explicit design.

Microsoft also treats revocation carefully. Its CVE-2023-24932 guidance warns that Secure Boot revocations can have persistent consequences. Once applied, they cannot simply be undone while Secure Boot remains in use. That’s a real reason why Microsoft has rolled related mitigations out in stages rather than treating them like an ordinary monthly update.

Enterprise guidance makes another dependency explicit. Adding Windows UEFI CA 2023 and untrusting Microsoft Windows Production PCA 2011 requires cooperation from device firmware. Differences among hardware and firmware therefore matter.

Revocation Supplies the Missing Shove

On my P16, requesting the PCA 2011 revocation was the move that finally altered the outcome. I would not claim that revoking PCA 2011 repaired a defective scheduled task. I cannot see enough of the task’s internal decision-making to verify that.

Nevertheless, the observable evidence supports a narrower and more useful conclusion. The machine had reached an intermediate Secure Boot state. Applying the revocation caused Windows and the firmware to complete the remaining transition work. Only then did the audit report the Secure Boot state as functionally complete and up-to-date.

That’s an important troubleshooting insight. When Secure-Boot-Update appears intransigent, the visible task state may be a symptom rather than the underlying cause. Certificate state, firmware state, Boot Manager signing and revocation state all need inspection.

Confirmation: (Mostly) Clean Garlin Check UEFI Results

That said, Garlin still reports two missing certificates.

These missing certificates serve different purposes from Windows UEFI CA 2023:

  • Microsoft UEFI CA 2023 signs third-party UEFI boot loaders and EFI applications.
  • Microsoft Option ROM UEFI CA 2023 signs third-party option ROMs.

They replace broader third-party trust previously supplied by the 2011 Microsoft UEFI certificate. Microsoft split the replacement into two certificates for finer control over third-party boot loaders and option ROMs.

Questioning the Final Garlin Repairs

However, the P16’s DB listing does not contain the old Microsoft Corporation UEFI CA 2011 certificate. Microsoft says the update task adds those two replacement certificates if the old Microsoft Corporation UEFI CA 2011 certificate exists in DB. It doesn’t so neither do they. Garlin’s script accurately observes that these two third-party certs are missing, but they don’t seem to interfere with proper boot behavior.

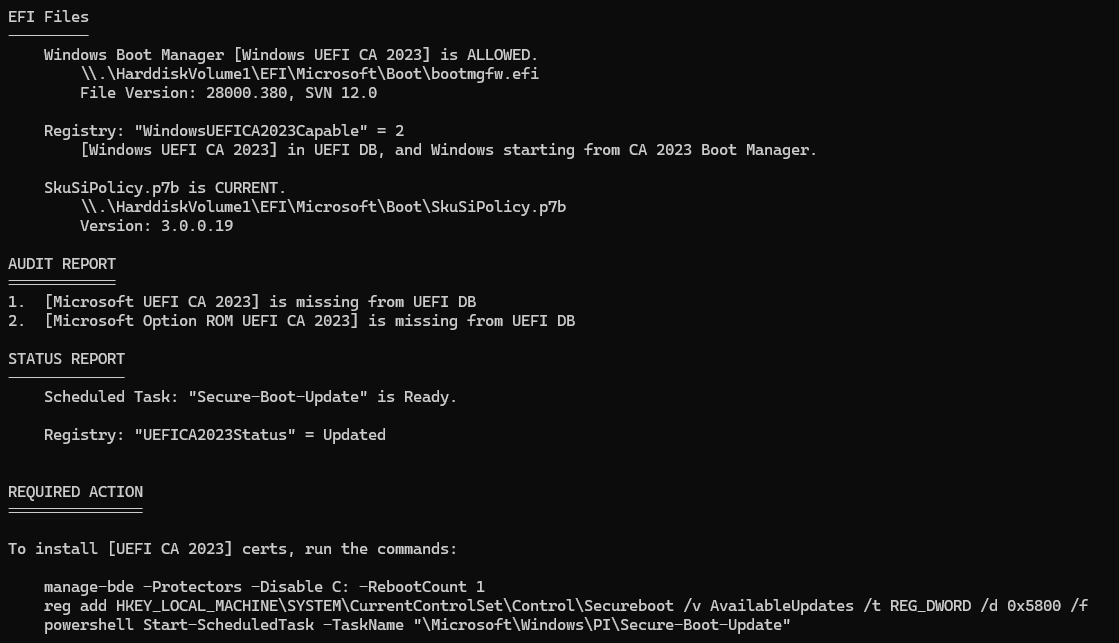
The decisive lines appear in the lead-in graphic as:

Windows Boot Manager [Windows UEFI CA 2023] is ALLOWED.
Registry: "WindowsUEFICA2023Capable" = 2
Registry: "UEFICA2023Status" = Updated
Windows BootMgr SVN 12.0
SkuSiPolicy.p7b is CURRENT.

The next screencap shows the tail-end of the Garlin check script results. I’ve run this repair three or more times and it never makes an impact on P16. That’s why I think it’s done, even though the check script still calls for those certs. Copilot says the 0x5800 modifier has a special meaning — namely:

  • 0x0800 requests installation of Microsoft Option ROM UEFI CA 2023 into DB.
  • 0x1000 requests installation of Microsoft UEFI CA 2023 into DB.
  • 0x4000 is a conditional modifier. It tells Windows to install those two certificates only if DB already contains the old Microsoft Corporation UEFI CA 2011 certificate.

Add ’em all together and  you get — wait for it — 0x5800. ‘Nuff said.

As far as I’m concerned, the P16 is fully updated and compliant. I had to do some learning to understand why. I did, and now I’m satisfied.

Further Reading

Microsoft Support, “How to manage the Windows Boot Manager revocations for Secure Boot changes associated with CVE-2023-24932” (KB5025885).
Microsoft Support, “Enterprise Deployment Guidance for CVE-2023-24932” (KB5053946).
Microsoft Support, “Updating Windows bootable media to use the PCA2023 signed boot manager” (KB5053484).
Microsoft Support, “When Secure Boot certificates expire on Windows devices” (KB5079373).

Facebooklinkedin
Facebooklinkedin

Benefits of Inventory Timing

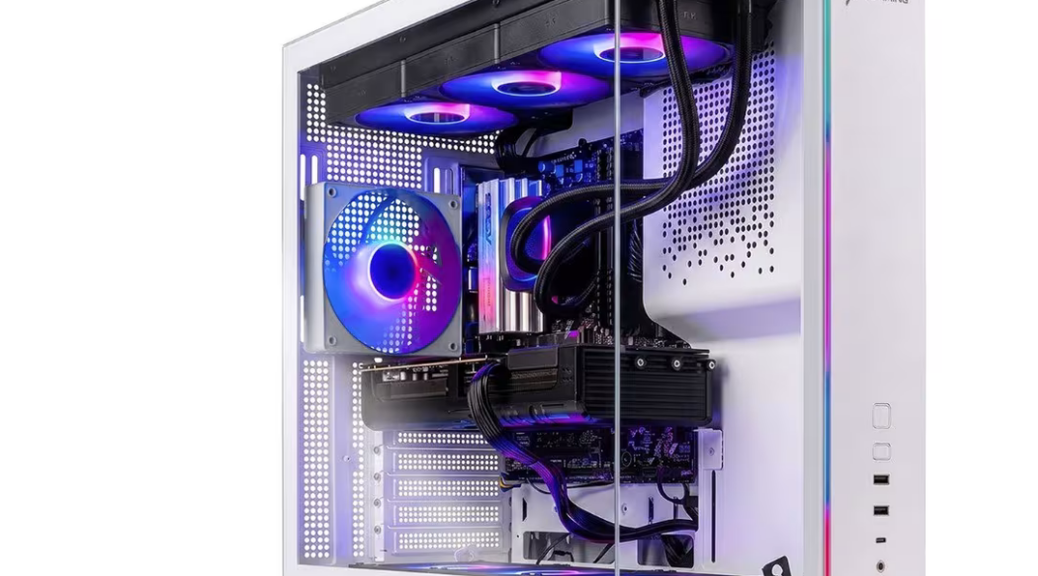
I had a real “How in the heck did they DO that?” moment this morning, reading over recent Tweaktown coverage.In this case (pun intended) PC pricing induces a self-builder (like your humble correspondent) to stop and check the numbers. This $2,430 Skytech gaming desktop at Walmart pairs an AMD Ryzen 7 9800X3D with an NVIDIA GeForce RTX 5070 Ti, 32GB of DDR5-6000, a 2TB NVMe SSD, a 360mm AIO and an 850W Gold power supply. “Hmmm,” I said to myself, “is this exploiting the benefits of inventory timing?”

By way of comparison, I priced a broadly comparable do-it-yourself configuration using recognizable retail components. Those parts came to $2,973.84 before tax. That puts the Walmart machine $543.84 below the DIY total, about 18 percent cheaper. Even removing the $139.99 Windows 11 Home license leaves DIY at $2,833.85. The prebuilt still leads by more than $400. Amazing!

Comparison Shows Possible Benefits of Inventory Timing

Here’s the comparison that caught my eye. The CPU, graphics card and memory alone total $2,013.90 at today’s prices: that leaves only $416.10 between those three retail parts and Walmart’s price for the whole shebang. Here’s a priced-out build list with today’s per-item “best cost” selections.

DIY PC vs. Walmart Skytech
Component DIY selection Price
CPU AMD Ryzen 7 9800X3D $444.00
GPU ASUS Prime RTX 5070 Ti 16GB $1,119.99
Motherboard ASUS TUF Gaming B850-Plus Wi-Fi $216.99
Memory 32GB DDR5-6000 CL30 $449.91
SSD Crucial E100 2TB Gen4 NVMe $249.99
CPU cooler Arctic Liquid Freezer III Pro 360 A-RGB $129.99
Case Lian Li Lancool 207 $82.99
Power supply Corsair RM850x 850W Gold ATX 3.1 $139.99
Operating system Windows 11 Home $139.99
DIY TOTAL $2,973.84
Walmart Skytech $2,430.00
PREBUILT ADVANTAGE $543.84

Why Say: Inventory Timing May Be at Work?

My best explanation for this sizable gap is inventory timing. Skytech may be building these systems from CPUs, memory, graphics cards and other components they acquired earlier. I assume that means at significantly lower costs than today’s per-item retail prices. Bulk purchasing could widen that gap.

That’s a premise rather than something documented. I don’t know Skytech’s acquisition cost or when its inventory was purchased. But the retail comparison makes this idea plausible. A system builder does not necessarily face the same replacement cost that confronts somebody ordering nine separate parts today.

That distinction matters especially around the holidays. A manufacturer with favorable inventory costs can turn older purchasing decisions into a current sales weapon. Instead of simply protecting margin, the vendor can pass some of the advantage along and produce a price that DIY buyers have difficulty matching.

Does DIY Even Compete/Compute Here?

The case for building your own PC isn’t entirely nixed. A self-build lets one choose the exact motherboard, SSD, power supply, cooler and graphics card. With the Skytech system, several of those specific makes and models are unspecified or may vary (and may not be to your liking). Component control has real value, particularly for buyers who care about firmware, expansion, acoustics or long-term serviceability.

A Deal Worth Considering

Still, $544 buys lots of component preference. At $2,430, I would have trouble justifying an equivalent self-build strictly on price. The Walmart system arrives assembled, includes Windows and carries a system warranty.

That makes this a useful lesson in PC purchasing. Current retail component prices don’t always dictate price for a prebuilt PC. Inventory has history. When a manufacturer bought well, and decides to turn that advantage into aggressive holiday pricing, yesterday’s inventory can become today’s bargain.

I’ve got to admit this is a good enough deal that I’m actually thinking it over. But with at least 4 strong, decently-equipped PCs here at Chez Tittel, I’ll probably have trouble selling to “The Boss.” But here in Windows-World, I can always dream about my next PC, knowing it’s a matter of “when,” not “if.”

Facebooklinkedin
Facebooklinkedin

Steps to an Ecology of Boot

With apologies to Gregory Bateson, I’m reminded of his work from the tangle of elements around booting to Windows 11 rescue media in the era of Secure Boot. Indeed, backups don’t count for much if their rescue media won’t boot. I rediscovered that old truth while testing Macrium Reflect X rescue media on my Lenovo ThinkPad P16. What looked like a simple USB boot test turned into a useful tour of modern Windows boot ecology. It also defined (for me, at least) the essential steps to an ecology of boot in today’s world.

Think about it: the word “ecology” fits. Modern booting isn’t one thing. It’s an interaction among firmware, Secure Boot certificates, revocation policy, boot files, BitLocker, virtualization-based security, the recovery environment, and even the particular USB flash drive you choose.

Steps to an Ecology of Boot: First, Update Rescue Media

My first concern was the Macrium rescue image itself. I had already been working on a PowerShell repair script, fixmrrdv6.ps1, to bring its boot components into line with current Secure Boot requirements. The script updates the external EFI boot manager and relevant files inside boot.wim.

Garlin’s Check_BootMedia.ps1 supplied the essential reality check. An earlier test showed the external Windows Boot Manager as BANNED even though components inside boot.wim were ALLOWED. After correcting the source and running version 6 of the repair script, the external boot manager, the WinPE boot manager, and winload.efi all reported ALLOWED. The boot manager showed SVN 12.0.

That was lesson one: a rescue UFD can look perfectly ordinary in File Explorer yet contain boot components that current Secure Boot policy won’t accept.

Step 2: Get the $#@^! UFD Recognized in UEFI

Next came hardware discovery. A SanDisk 32 GB UFD (USB Flash Drive) didn’t appear in the P16 F12 boot menu. I moved it from one USB-A port to another. No joy. I also encountered the curious “USB FDD” boot choice while working through Windows recovery options. Selecting it did not produce a successful rescue boot.

At that point the problem had stopped looking purely like Secure Boot. If firmware won’t enumerate a device as a boot candidate, fixing the files on that device won’t go anywhere.

So I changed media. I built fresh Macrium rescue media on other UFDs, including a Mushkin Ventura Pro. Ultimately, an ADATA S102 became the device that successfully booted the P16. Go figure!

Step 3: Slogging Through Security Layers

The P16 sports a full complement of modern Windows protections. Secure Boot was on. BitLocker protected C:. Virtualization-based security and Device Guard were in the mix. That’s good for normal operation, but it introduces multiple variables when testing alternate boot media.

I suspended BitLocker protection for the experiment. I also temporarily turned Device Guard/VBS off. That did not make Windows “recognize USB.” Instead, it removed another security and code-integrity variable while testing whether or not the repaired rescue environment could actually start.

Importantly, Secure Boot stayed on. That made the successful test meaningful. I wasn’t simply bypassing the very mechanism I wanted the rescue disk to comply with.

Step 4: The Boot Circle Shows Up from the Rescue Disk

With the ADATA rescue UFD in place and the test conditions sorted out, I initiated the alternate boot. The P16 went black for quite a while. Then the familiar spinning circle appeared. Finally, Macrium Reflect’s WinPE rescue environment appeared.

That was the result I wanted. I opened a command prompt inside WinPE and later used wpeutil reboot to return the P16 to Windows.

Back in the running OS, I restored the normal protection state. BitLocker once again reported ProtectionStatus On. Subsequent checks showed Secure Boot on and virtualization-based security running.

What Did I Learn From This Tapdance?

The biggest lesson is that “bootable USB” is no longer a yes/no thing. A UFD may contain the right partition, filesystem, EFI directory, boot.wim, and loader files, yet still fail somewhere along the path from firmware enumeration to Windows PE.

Current Secure Boot policy makes its contents matter. BitLocker makes boot-state changes matter. Device Guard and VBS add another enforcement layer. Firmware decides whether the UFD works at all. And apparently the physical flash device matters, too.

That last point remains a mystery. The ADATA S102 worked where the Mushkin Ventura Pro did not. I don’t yet have a satisfying technical explanation for that. What I do have is a repeatable successful test using the ADATA. So that’s what I’ll use.

That’s troubleshooting in a nutshell. Change one variable where possible. Verify the state at every layer. Keep good tools handy. And never assume your rescue disk can rescue anything until you’ve actually booted it and seen it work. Here in Windows-World, rescue isn’t guaranteed unless you check it before the brown stuff hits the whirling blades!

Facebooklinkedin
Facebooklinkedin

Scripting Macrium Rescue Disk Repair

Here’s something I’ve been chewing on for the past few weeks. I’ve had help from a persistent and curiously passive interlocutor at ElevenForum.com. I still use Macrium Reflect to back up at least half of my PC fleet.

For whatever reason, the Macrium Software team has yet to update its Rescue Disk creation to accommodate Secure Boot requirements. That’s what led me to scripting Macrium Rescue Disk repair using Copilot and PowerShell. Therein hangs today’s post…

What’s Involved in Scripting Macrium Rescue Disk Repair?

Basically, I asked Copilot to build a PowerShell script to fix the Macrium Rescue Disk for Secure Boot. Why? I use Secure Boot on all my PCs.

I can’t restore a Reflect boot image unless the Rescue Disk will actually BOOT the target PC. Only then can I perform the restore operation.

For the record, I’m using Macrium Reflect X, not the older versions numbered 8.x or lower. Working with Copilot, I had to chunk through three, then four versions before the script worked on my PC.

That PC is Flo6, my B550-based desktop. It has an MSI MAG Tomahawk MAX motherboard, Ryzen 7 5800X, NVIDIA RTX 3070 Ti, and 64GB RAM.

Using Copilot Requires LOTS of Trial and Error

The output from the script itself documents what it does pretty well, so I reproduce it here:

==============================================================
  fixmrrdv6.ps1  --  Secure Boot SVN Repair Tool              
==============================================================
   [>>] Validating target drive: G:                                                                                                                       
       [OK] Drive label  : ESD-USB                                                                                                                       
       [OK] File system  : FAT32
       [OK] Size         : 14.4 GB
       [!!] Label 'ESD-USB' does not contain MACRIUM -- verify correct drive.
   [>>] Locating boot.wim on rescue media                                                                                                                 
       [OK] Found WIM    : G:\sources\boot.wim                                                                                                           
       [OK] WIM size     : 557.2 MB
   [>>] Locating Secure Boot source files from live Windows
       [OK] External source: C:\Windows\Boot\EFI_EX\bootmgfw_EX.efi
       [OK] WIM source     : C:\Windows\Boot\EFI_EX\bootmgfw_EX.efi
       [OK] Winload source : C:\Windows\System32\winload.efi
       [OK] Backup root    : C:\Users\ed\AppData\Local\Temp\FixMRRD_Backups_20261026_155946
   [>>] Replacing external bootmgfw.efi on USB
       [OK] Backed up: bootmgfw.efi -> C:\Users\ed\AppData\Local\Temp\FixMRRD_Backups_20261026_155946\ExternalUSB\bootmgfw.efi
       [OK] Replaced: bootmgfw.efi from EFI_EX\bootmgfw_EX.efi
   [>>] Patching boot.wim (index 1) with Secure Boot files
       [OK] Mount directory  : C:\Users\ed\AppData\Local\Temp\FixMRRD_WimMount_20261026155946
       [!!] Mounting WIM (this may take a minute)...
       [OK] WIM mounted successfully.
       [OK] Backed up: bootmgfw.efi -> C:\Users\ed\AppData\Local\Temp\FixMRRD_Backups_20261026_155946\WIM\bootmgfw.efi
       [OK] Patched: bootmgfw.efi
       [OK] Backed up: bootmgfw_EX.efi -> C:\Users\ed\AppData\Local\Temp\FixMRRD_Backups_20261026_155946\WIM\bootmgfw_EX.efi
       [OK] Patched: bootmgfw_EX.efi
       [OK] Backed up: winload.efi -> C:\Users\ed\AppData\Local\Temp\FixMRRD_Backups_20261026_155946\WIM\winload.efi
       [OK] Patched: winload.efi
       [!!] Committing and unmounting WIM (this may take a minute)...
       [OK] boot.wim patched and committed successfully.

==============================================================
  All done! Secure Boot SVN repair completed successfully.
  Run check_bootmedia.ps1 against the USB to verify ALLOWED.
==============================================================

To debug this script, I kept catching error messages as it ran, reporting them to Copilot, and re-running rewritten versions until it produced a clean Rescue Disk on Flo6. How did I define that? By running Garlin’s check_bootmedia.ps1 script against it until it returned a clean result (all boot managers use CA 2023, show up as ALLOWED, use SVN 12.0). And indeed it works on Flo6 right now just fine.

What Works for Me, May Not Work for YOU

What I’ve learned from my interlocutor on ElevenForum.com is the following. Though the script runs on Flo6, it doesn’t run on his PC. Based on the errors he’s reporting, I think I know what’s going on. Writing files into a mounted WIM is tricky, as I’ve learned, and requires extensive mucking about with permissions. System ownership must be taken over, writing work done, then restored to pristine condition. This takes work and some understanding of how ACLs and the Trusted Installer work in modern Windows OSes (10 and 11, basically, though the same behaviors also hold in current Windows Server versions).

When things go wrong for me with a script like this one, I attack them with Copilot until they work. My interlocutor, apparently, isn’t inclined to do this himself. But that’s what it takes to make things work on YOUR PC here in Windows-World: a dogged determination to keep iterating until the error messages no longer appear, and the resulting functionality does what you want it to do.

Post some comments here to let me know if you’re OK with this “exercise is left to the reader to fully complete” approach. Those who really want the script to fix their Macrium Reflect X Rescue Disks can ask for it, and I’ll send it to them. But they’ll have to be ready to make it work on their PCs to achieve its intended use!

Facebooklinkedin
Facebooklinkedin

MS Store Sees Update Coming, But…

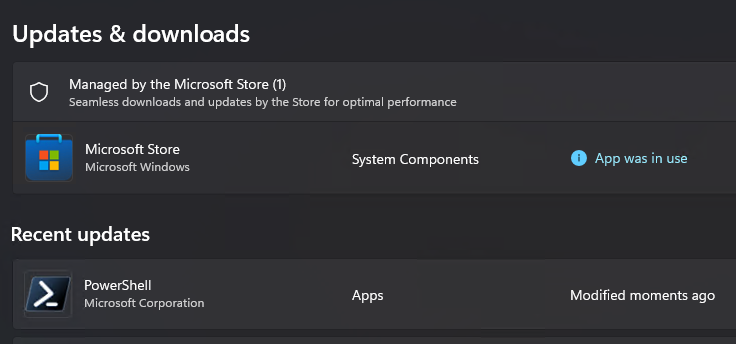
It’s definitely a Monday. I’ve got interesting oddities popping up right and left. Take a look at the intro screenshot. When I run “Check for updates” from the Updates and Downloads tab in MS Store, it sometimes tells me that it itself needs an update, but couldn’t run because the “App was in use” (as shown). Funnily enough, if I close the app then re-open it, that pending update no longer shows but is also missing in the “Recent updates list” below. Thus, MS Store sees update coming, but no longer see it when it’s done. Weird…

Yes: MS Store Sees Update Coming, But No History

I had to ask Copilot what it thought was going on. To my relief, it confirms that indeed this particular self-update goes untracked:

Once the update completes, the Store process reloads into its newly installed package. The Updates & downloads page then refreshes from inside that replacement package. Apparently, the Store does not reliably copy its own completed update into the user-facing Recent updates list.

So it seems to be a case of “Lost in transition” rather than “Lost in translation.” Just another interesting oddity to notice. It doesn’t seem to exact any consequences, as far as I can tell.

Self-Updates Are Almost Always Interesting

In working with WinGet over the past 6-plus years, I’ve noticed that things get interesting when running packages have to handle their own updates. That’s what I call a self-update. For example, WinGet itself (Microsoft.AppInstaller), PowerShell, and Windows Terminal, all get a little flustered when they themselves handle updates in an active Windows Terminal session.

Usually, the right way to straighten things out is to close them, then re-open them. Sometimes, a reboot may be needed to untangle the thorniest of self-updates. But gosh, this is the first time I can recall that the update history itself drops a stitch and misses its own incremental advancement. That’s odd, even here in Windows-World. But it’s all part of its strange charm…

Facebooklinkedin
Facebooklinkedin