Category Archives: Cool Tools

UniGetUI Handles Discord Updates

In my September 16 post, “WinGet Mistakenly Reports Discord as Pinned,” I covered a quirk in how winget labels certain packages. I was reminded of same, as I observed that UniGetUI hanldes Discord updates easily and directly. If winget marks Discord as pinned and skips it, how can UniGetUI update it anyway? Let me ‘splain it to you.

How UniGetUI Handles Discord Update, While WinGet Fails

It is a handling difference that distinguishes the two package managers. Actually, WinGet itself stumbles only when using update --all. WinGet actually CAN handle a Discord update but it has to be commanded correctly and directly. UniGetUI uses WinGet to get (at least some of) its work done (also works with Chocolatey, Scoop, etc.). The trick turns out to hinge on how WinGet is told to upgrade Discord. The blanket approach just described fails because of a manifest flag (see 9/16 post for deets). Winget simply skips over that upgrade.

UniGetUI does things differently. Under the hood, it calls winget using an explicit package ID for each app that needs an update. For Discord it works just as if it had entered

winget upgrade --id Discord.Discord --include-pinned

at a command line (cmd.exe or PowerShell). In fact, WinGet will update Discord if you use similar syntax, to wit:

winget upgrade --id Discord.Discord --force

Manual Override Is a One-Off Avventura

Please note: the preceding command string is a one-time override. The RequireExplicitUpgrade: true flag that causes WinGet to skip over Discord for WinGet upgrade --all stays in place. Future winget upgrade –all runs will still skip Discord, so you would need to repeat the command each time you wanted to force that update manually.

UniGetUI’s approach turns this winget blind spot into a non-issue for anyone who prefers a GUI workflow. I’m actually coming to like this program more and more because of its consistent, user-friendly package handling. But WinGet remains number one in my heart because it’s command-line native, and readily susceptible to scripting and automation.

Facebooklinkedin
Facebooklinkedin

Powershell Update Goes Sideways

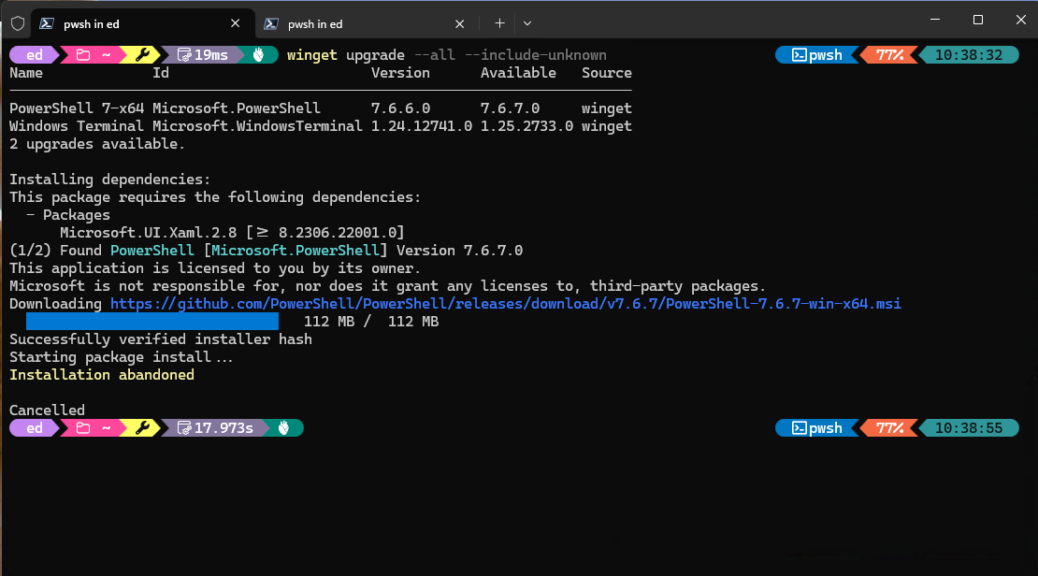
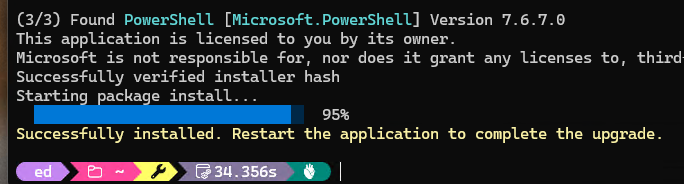
Interesting doings in the Windows Terminal PowerShell world. Running WinGet in that environment just now, I updated PS. Not only did that activity produce an “Installation abandoned” error msg, it initially threw up cmd prompt instead of PS when I clicked the plus sign to launch a new WinTerm session. Alas, it looks like this PowerShell update goes sideways (and more so on some PCs).

Ways PowerShell Update Goes Sideways

First, let’s survey the landscape. Windows PowerShell 5.1 is built into Windows and goes nowhere. It is a system component, not something you update through a package manager. PowerShell 7.x is a completely separate, side-by-side install. It lives in its own directory and uses its own executable, pwsh.exe.

The standard command for updating PowerShell 7.x is clean and simple. You open a terminal and run winget upgrade --id Microsoft.PowerShell. However, what looks simple on the surface can hide a lot of failure modes underneath.

Updates can stall mid-stream, roll back without a clear explanation, or appear to succeed while doing nothing at all. That last scenario is especially maddening. You see a success message, then run pwsh --version and get the old build number staring back at you. Something broke during the install, and winget did not catch it.

Oh No! Installation Abandoned…

I’ve seen this error message (see lead-in graphic) before. Normally, that means the PS installer has lost its connection to Winget via PowerShell and WinTerm. You can often see the PS installer window open, still running, and finishing its work. Closing, then re-opening WinTerm usually sets things back to rights.

Not this morning, on my Flo6 desktop (B550 mobo with AMD Ryzen 7 5800X CPU). After the upgrade, a new PS session launched cmd prompt instead. WinTerm lost its path to the pwsh.exe executable. When I went to look at its profile, it showed as empty. So I had to delete it, and recreate it, then point to the PowerShell 7 icon. That fixed things right up.

That Worst Case Isn’t Ubiquitous

When I updated PS on the Lenovo ThinkPad P16 Gen 1 mobile workstation, I got the same “installation abandoned” error message. But when I opened a new PS session (using the menu bar “+” control) the new version popped right up in a proper PowerShell pane.

I’m not sure why some machines act out more than others when the PS install goes sideways. Shoot! It could have been cosmic rays. But whatever happens, you can fix it if you check the profile and make sure it’s properly defined. Here in Windows-World knowing what to fix and how to fix it goes a long, long way. This morning, it went far enough to set things back up properly on Flo6. May it do the same for you, should you need it to!

One More Thing…

Just ran the same update on the ASUS Zenbook A14 (Snapdragon X ARM CPU). Completed successfully! I’m starting to think that platform diffs may play into this situation. The AMD platform failed and carried a persistent error state. The Intel platform failed, but recovered. And the ARM platform sailed right thru. Go figure!


Facebooklinkedin
Facebooklinkedin

Another OOO, Another Catchup

OK then, I’ve been away from home since October 1. Sorry to report it was to attend a memorial service for my brother-in-law, Mike Carey, who succumbed to lung cancer on September 19. Now that I’m back in the saddle, my first task was to check and apply all outstanding updates to the Windows fleet here at Chez Tittel. That sort of make my marching orders read “Another OOO, another catchup.” Let me tell you what that meant this morning…

Working Through Another OOO, Another Catchup

There are 8 PCs in the fleet at present. Two AMD, one Snapdragon X, the rest Intel. I ran through the gamut of update checks on each one and did the necessary.

Name WinGet DSA PMP Other Total
X12 5 3 2 0 10
P16 2 0 1 0 3
X380 9 0 1 1 11
Flo6 4 0 1 2 7
P3Ultra 4 1 3 0 8
AsusA14 5 0 1 0 6
Ryzen 11 0 1 1 13
D7080 3 0 3 3 9
Totals 43 4 13 7 67

In the column heads PMP = Patch My PC Home Updater and DSA = Intel Driver & Support Assistant. As you can see, I had a decent number of updates to handle (67 for 8 machines averages between 8.0 and 8.5). Under “Other,” I accessed Lenovo Vantage, Dell Command Update and the ASUS update facility, on related systems. And both of my NVIDIA-equipped PCs (RyzenOfc and Flo6) got GPU updates. But it’s all taken care of now.

Now What’s Next?

I keep up with WinGet on a more or less daily basis. The other stuff falls into the “as I read about it in the news” or “once a week” category. So I should be good until next week for now.

It’s good to be back. I look forward to catching up and commenting on recent Windows news, updates and introductions. Stay tuned, and I’ll tell you more.

Facebooklinkedin
Facebooklinkedin

Fixing Macrium Rescue Disk

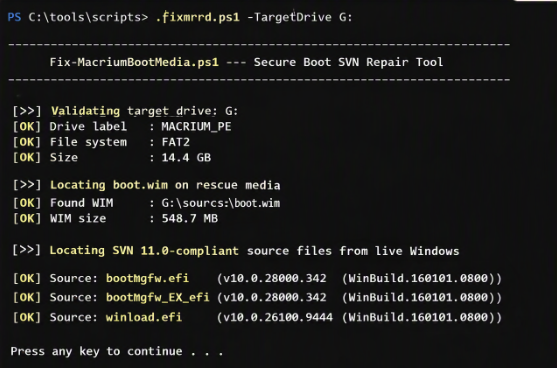
Microsoft updated its Secure Boot revocation database (DBX) in mid-2026. That update requires Boot Manager binaries to carry a minimum Security Version Number (SVN) of 11.0. It also bans the older “Production PCA 2011” signing certificate. Rescue media that Macrium Reflect X builds fails both tests out of the box. That means with Secure Boot enabled, the Reflect’s boot media won’t work. That’s why I’m writing today about what’s involved in fixing Macrium Rescue Disk.

Most important, this post walks you through a PowerShell script named fixmrrd.ps1 that fixes all three BANNED files in a single pass. Buckle up! There’s LOTS of ground to cover…

Why Fixing Macrium Rescue Disk Is Necessary

Macrium Reflect X builds its WinPE rescue environment from the Windows ADK (Assessment and Deployment Kit). The ADK ships once per Windows release and never gets Patch Tuesday updates. Its boot files stay frozen at the SVN level they carried on release day.

For Windows 11 24H2, the WADK 11 ADK shipped with boot files at SVN 2.0. The current DBX floor is SVN 11.0. That nine-version gap is the core problem that requires fixing.

The standard boot manager file, aka bootmgfw.efi that lives under C:\Windows\Boot\EFI\ also carries the banned Production PCA 2011 certificate. Even when the SVN is correct, that certificate triggers a hard BANNED result. Garlin’s check_bootMedia.ps1 diagnostic tool makes both problems visible immediately.

Introducing fixmrrdv2.ps1

fixmrrdv2.ps1 bridges the gap Macrium leaves open. It pulls every replacement file from your live, fully patched Windows 11 installation. Those files already meet the SVN 11.0 requirement and carry the correct Windows UEFI CA 2023 certificate. It’s a v2 version because @Monica1491 over at ElevenForums pointed out an error that I fixed.

Here is what the script does at each step:

  1. Validates the target USB drive and confirms it carries a MACRIUM label.
  2. Locates boot.wim on the rescue media, typically at sources\boot.wim.
  3. Identifies three source files from your live Windows installation: bootmgfw.efi, bootmgfw_EX.efi, and winload.efi. It reports the version number of each file.
  4. Replaces the external bootmgfw.efi on the USB EFI partition. It uses the EX variant (bootmgfw_EX.efi) as the source — not the standard bootmgfw.efi. The standard file carries the banned Production PCA 2011 certificate. The EX variant carries the required Windows UEFI CA 2023 certificate.
  5. Mounts boot.wim using DISM. Then it adjusts ACLs on the internal target files. WIM images lock their contents with restrictive ACLs. Even Administrator hits an access-denied error without a takeown and icacls step first.
  6. Replaces bootmgfw_EX.efi and winload.efi inside the mounted WIM.
  7. Commits the changes and unmounts the WIM. If any step fails, DISM discards the mount and leaves the original WIM intact.

The script backs up every replaced file with a timestamped .bak_ suffix before touching it. Color-coded [OK], [!!], and [FAIL] status lines show progress at each step.

Before You Run the Script…

There are four prerequisites apply before you run fixmrrdv2.ps1.

  • Run as Administrator. DISM mount operations require elevation.
  • Use Windows PowerShell 5.1 (powershell.exe). Do NOT use PowerShell 7.x (pwsh.exe). The DISM /Mount-Image command does not work correctly under PowerShell Core. The script detects PS 7.x automatically and exits with a clear message if you start it from the wrong shell.
  • Your Macrium rescue USB must be plugged in and assigned a drive letter. Note that letter before you start.
  • Your execution policy must allow local scripts. Run this in an elevated PS 5.1 window if needed:

Set-ExecutionPolicy -ExecutionPolicy RemoteSigned -Scope CurrentUser

Download fixmrrdv2.txt from its OneDrive link (read only). Rename it to fixmrrd.ps1. Place it in a convenient location, such as C:\tools\scripts\.

Running the Script…

Open an elevated Windows PowerShell 5.1 window. Navigate to the folder holding fixmrrd.ps1. Then run:

.\fixmrrd.ps1 -TargetDrive G:

Substitute your actual rescue drive letter for G:. If you omit -TargetDrive, the script prompts you for it.

The script runs without further interaction. The DISM commit step takes the longest — typically 30 to 60 seconds. Do not interrupt that step.

Each replaced file gets a timestamped .bak_ backup before the script writes anything new. You can restore any original file by renaming the matching backup.

One timing note: the script reports source file versions from C:\Windows\Boot\EFI\ and C:\Windows\Boot\EFI_EX\. You may notice the version number on the USB after copy differs slightly from what the script reported. This is a FAT32 metadata quirk. The SVN level is what really matters, and transfers correctly.

Verifying Results

Run Garlin’s check_bootMedia.ps1 against the drive when the script finishes:

.\check_bootMedia.ps1 G: -audit -verbose

A correctly fixed drive shows all three boot files as ALLOWED:

USB Drive g: "MACRIUM_PE"
    Windows Boot Manager [Windows UEFI CA 2023] is ALLOWED.
        g:\EFI\Microsoft\Boot\bootmgfw.efi
        File Version: 28000.367, SVN 11.0

    boot.wim:1 (WinPE 26100.1)
        Boot Manager [Windows UEFI CA 2023] is ALLOWED.
            \Windows\Boot\EFI_EX\bootmgfw_EX.efi
            File version: 28000.367, SVN 11.0

    \Windows\System32\winload.efi is ALLOWED.
        File version: 26100.9444

If any file still shows BANNED, check that you ran the script in PowerShell 5.1 with elevation. Re-run if needed — the backup files let you roll back safely.

The Net-Net: Working Rescue Disk

This is a product gap in Macrium Reflect X, not a user error. Macrium builds from ADK components that Microsoft does not update through Patch Tuesday. The recoverydrive.exe tool that ships with Windows sources its boot files directly from the live OS. Macrium does not. Until Macrium ships a fix that closes that gap, fixmrrd.ps1 fills it. It ticks me off, and that’s why I decided to script my way around it.

Keep this script on hand. The next time you rebuild a Macrium rescue drive, perhaps after a major Windows update or a new ADK release, you will need it again. The whole process takes under two minutes once you know the steps. Here in Windows-World, when vendors don’t fix their stuff, we users must sometimes step in to help out. Cheers!


Facebooklinkedin
Facebooklinkedin

Removing Stubborn Acrobat Pin

I keep learning more and more about hidden wrinkles in WinGet. I guess that’s because I use it every day, and notice when things get hinky. Today, I noticed my pin on Adobe Acrobat got stuck like Schrodinger’s cat: it was there and not-there at the same time. Ultimately, this had me removing stubborn Acrobat pin, as normal methods couldn’t do their job. Let me explain…

What’s Involved When Removing Stubborn Acrobat Pin?

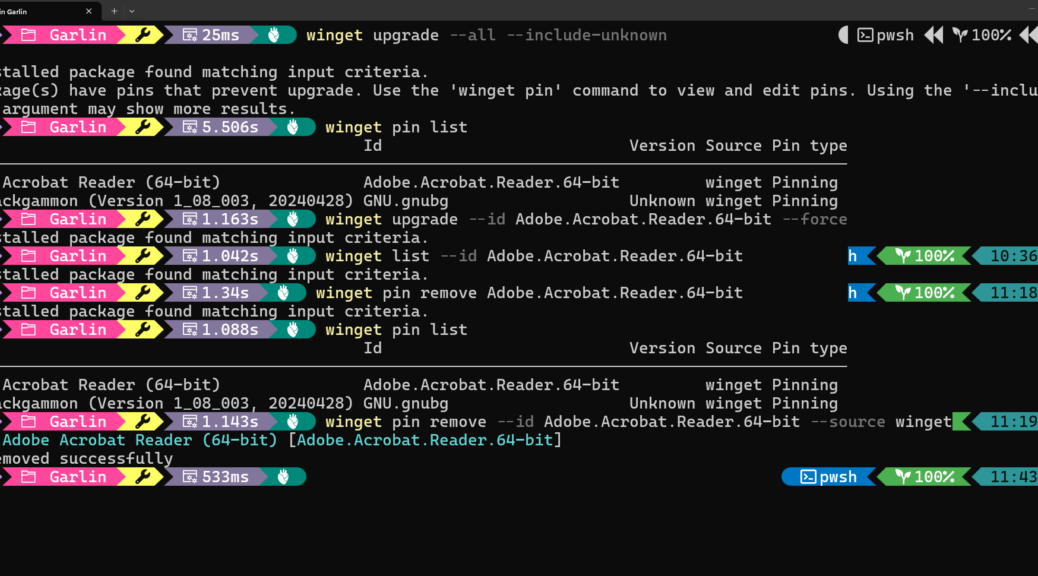
Take a look at the WinTerm screen capture that starts off this blog post. After running winget upgrade ... I got a message “1 package(s) have pins that prevent upgrade.” Flo6 has 2 pins right now and one of them has no internal version number (GNU Backgammon) so I knew the affected package must be Adobe Acrobat. You can see both packages as output to the winget pin list, in fact.

But as you can see in the next two lines, neither winget list --id... nor winget pin remove recognized Adobe.Acrobat.Reader.64-bit as a valid package name. That’s decidedly odd, because that’s the name that shows up in winget pin listoutput shown earlier.

Turns out that’s a thing. It’s a short form versus long, explicit form discrepancy.

Why the Short Form Fails

When you run winget pin remove without explicit flags, winget uses positional argument matching. It tries to match the string Adobe.Acrobat.Reader.64-bit against its installed packages database first. It does not go straight to the pin store.

If WinGet cannot find a recognized installed package entry for that string, it stops. It bails out before it ever reaches the pin database. The pin record sits untouched.

This mismatch happens for a specific reason. Adobe Acrobat was likely removed through Windows Settings or Add/Remove Programs, not through winget uninstall. Winget never got the chance to clean up its own records. So the installed-package record disappeared, but the pin record survived in winget’s separate pinning.db database file.

That gap between the two databases is the root cause of the error. The fix is to route Winget around that gap entirely.

The Fix: Explicit Flags

The solution is to be explicit with WinGet. To do that, add two flags to the command: –id and –source. Together, they change how winget searches. Use this exact command:

winget pin remove --id Adobe.Acrobat.Reader.64-bit --source winget

Here’s how this works: The --id flag forces WinGet to look up the package by its exact manifest identifier. The --source flag tells WinGet to look specifically in the winget source. Together, they bypass the installed-package correlation step and go straight to the pin store.

The output confirms it works. You see “Found Adobe Acrobat Reader (64-bit) [Adobe.Acrobat.Reader.64-bit]” followed immediately by “Pin removed successfully.” Run winget pin list one more time to confirm the pin is gone. It will be.

This is the cleanest way to use winget pin remove whenever a package no longer has a matching installed record. Keep those flags in your back pocket.

Take the Long Way Home

When winget pin remove fails with “No installed package found,” the short form is matching against the wrong database. Adding
--id and --source redirects it straight to the pin store, where it needs to go. Always uninstall packages through WinGet when you can. That keeps its databases in sync and prevents this mismatch from happening in the first place. A little discipline now saves a lot of troubleshooting later, and now you know exactly what to do when things go sideways despite your best efforts. A not unfamiliar sensation to those who, like me, run in the halls of Windows-World.

Facebooklinkedin
Facebooklinkedin

WinGet Mistakenly Reports Discord as Pinned

Here’s a scenario many Windows users will recognize. You open a terminal and run winget upgrade to freshen up your apps. Everything looks normal — until you spot Discord sitting there labeled “pinned.” You never pinned it. You have no idea why it shows up that way. Sound familiar? Turns out that WinGet mistakenly reports Discord as Pinned for its own, somewhat murky reasons.

This WinGet Discord pinned situation surprises a lot of people. It looks wrong, or like WinGet won’t update a much-used app. Neither is true.

Take a breath. Discord is fine. WinGet is fine. There’s a perfectly logical explanation — and once you see it, the whole thing makes complete sense. Let me fill  you in…

Why WinGet Mistakenly Reports Discord as Pinned

WinGet uses the “pinned” label for two very different situations, and it doesn’t distinguish between them visually. The first situation is one you control: you run winget pin on a package, and WinGet holds that app at its current version. That’s an intentional, user-driven pin.

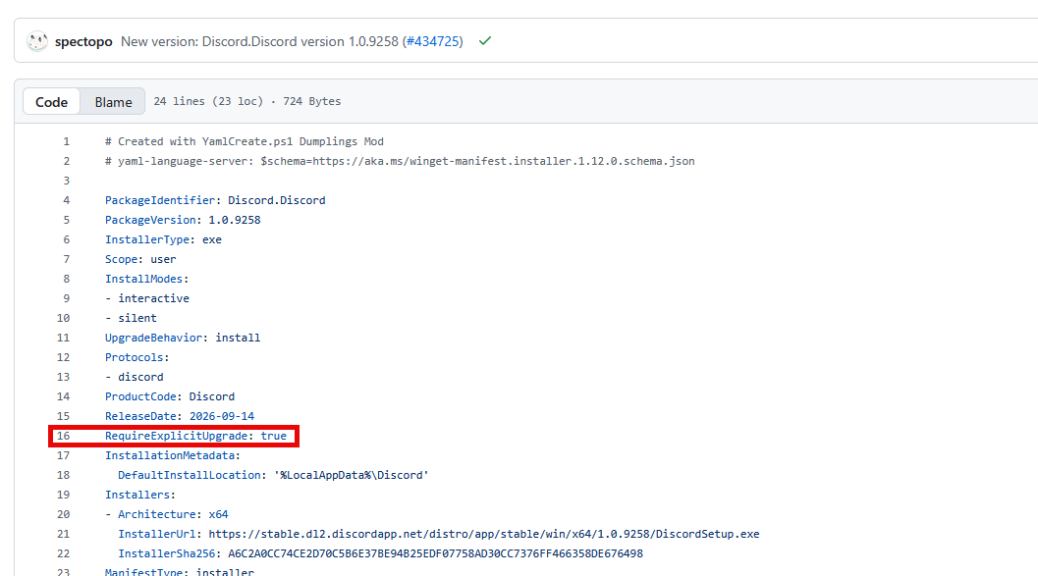
The second situation involves the app’s own manifest. Package maintainers can set a field called RequireExplicitUpgrade to true inside their installer’s YAML file. When WinGet sees that flag, it skips the package during bulk upgrade runs. Then, it labels it as “pinned” in the output.

Discord’s manifest resides in the winget-pkgs repository. ICYDK, that’s the Microsoft community Windows Package Manager manifest repository on GitHub. There, its manifest carries RequireExplicitUpgrade: true across many versions, including 1.0.9005, 1.0.9166, and 1.0.9188. WinGet groups both user-set pins and manifest-driven flags under the same display label. That shared label is the root of all this kerfluffle.

Why Discord Sets RequireExplicitUpgrade

Discord ships with its own built-in auto-updater. Most of the time, Discord updates itself quietly in the background without you lifting a finger. It doesn’t need WinGet’s help to stay current. It runs by default each time you open the app (or restart your PC).

Setting RequireExplicitUpgrade: true in the manifest tells WinGet to stand down during bulk winget upgrade runs. This prevents WinGet from downloading and launching a full installer that could interfere with Discord’s own update mechanism. Two updaters competing for the same app can be a recipe for trouble.

This is actually a smart, deliberate design choice. Thus, it’s not a bug, nor an oversight. The Discord team and the winget-pkgs maintainers made a deliberate call to keep things tidy. WinGet and Discord each do their own job, without stepping on each other.

How to Check the Discord Manifest

Want to see Discord’s package details for yourself? Start with this command:

winget show --id Discord.Discord

This output gives you useful metadata — the current version, publisher, installer URL, SHA256 hash, and release date. What it does not show is the RequireExplicitUpgrade field. winget show surfaces display metadata, not every field in its YAML manifest.

The file Discord.Discord.installer.yaml does not exist on your local PC. It lives only on GitHub. To find it, go directly to this URL in your browser. (Swap in whatever the current version number is for 1.0.9258 if needed.) Once there, look for RequireExplicitUpgrade: true in the YAML. That single line is what tells WinGet to treat Discord as a skip-by-default package during bulk upgrades. You can see it highlighted in the lead-in graphic at line 16 of that YAML file, in fact.

Upgrading Discord Through WinGet Anyway

Maybe you want WinGet to handle the Discord update on your terms. No problem. You can override the RequireExplicitUpgrade flag with a single targeted command:

winget upgrade --id Discord.Discord --force

This tells WinGet to update Discord explicitly, bypassing the manifest flag just for this one run. It’s a clean, safe way to push a WinGet-managed update when you want one.

That said, most of the time you won’t need to bother. Discord’s own updater does its job reliably and quietly. The WinGet Discord pinned label looks alarming, but your Discord client is almost certainly already up to date. Check the app’s version in its settings if you want confirmation.

WinGet Category Conflation Explains All

The “pinned” label WinGet shows for Discord is not a real user-set pin. Again, you did nothing wrong, and nothing is broken. It reflects the RequireExplicitUpgrade: true field baked into Discord’s own manifest That tells WinGet to step aside and let Discord’s built-in updater do its thing. Once you understand the distinction, WinGet’s behavior makes perfect sense. This behavior is simply misreported as “pinned” not “RequireExplicitUpgrade.”

Now that you know what’s going on, you can look at that “pinned” label and nod knowingly instead of scratching your head. That’s what understanding tools is all about. That makes you a sharper and better-informed inhabitant, here in Windows-World.

Facebooklinkedin
Facebooklinkedin

Strange DirectX Pin on Flo6

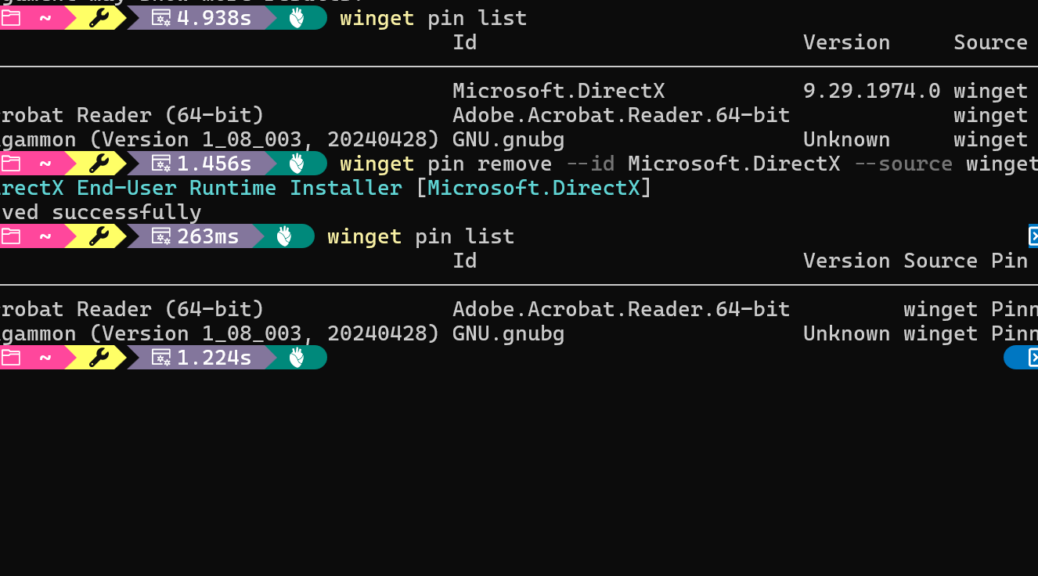
I was doing a routine check of my WinGet pin list on Flo6 just now (ICYMI, Flo6 is my production desktop). After running winget pin list I spotted three pinned packages. Two of them I recognized immediately. Adobe Acrobat Reader (64-bit) and GNU Backgammon  I pinned myself, on purpose. But the third one stopped me cold. It showed Microsoft.DirectX at version 9.29.1974.0. I had never pinned that. Why did I see this strange DirectX pin?

How I Got a Strange DirectX Pin on Flo6…

First, let me share some background. Modern DirectX, meaning DirectX 11 and DirectX 12, is baked directly into Windows. Windows Update manages it entirely. Winget does not install, update, or remove it. How, then, did it make its appearance?

The Microsoft.DirectX package from the WinGet community catalog is something else entirely. It refers to the DirectX End-User Runtime redistributable, specifically its June 2010 release. That’s the last one MS ever shipped.

Indeed, Version 9.29.1974.0 is the final, frozen-forever build. It’s unchanged since 2010. Back in the day, games and apps from that era bundled this runtime to pull in legacy components. Think D3DX9, XAudio2, and XInput. On most modern Windows systems, this redistributable is obsolete and irrelevant.

The Source of This Strange Pin May Be…

Here’s where things get weird. The Microsoft.DirectX manifest in the WinGet community catalog had a long-running typo. For a while, it listed the package version as 9.29.1974.1 instead of the correct 9.29.1974.0. A community contributor eventually caught the error and submitted a pull request to fix it.

Once that fix merged into the catalog, WinGet suddenly saw a mismatch on affected machines. The catalog now declared 9.29.1974.0 as current. The installed runtime also reported 9.29.1974.0. So far so good. But the metadata around the install technology did not reconcile cleanly. Windows owns and controls the DirectX runtime. WinGet does not.

Winget could neither upgrade the package nor cleanly resolve the discrepancy. So it did the next best thing. It quietly added a Pinning-type pin to suppress its spurious upgrade prompt. That kept its noise out of winget upgrade --all output. In short, winget added the pin to stop nagging itself about a package it cannot actually manage. I have to laugh about that, give me a moment…

Removing the DirectX Winget Pin Is Safe

The good news here is straightforward. This pin is purely administrative. WinGet created it as a workaround for its own catalog inconsistency. It was never protecting anything vital.

Removing the pin leaves the DirectX runtime alone. The actual runtime stays right where it is. Windows Update continues to manage it, same as always. Better yet, the phantom upgrade version, 9.29.1974.1, is already gone from the WinGet catalog. Removing the pin won’t spur any bogus upgrade attempts. Nothing bad is waiting to happen.

The command to remove it is simple:

winget pin remove --id Microsoft.DirectX --source winget

As you can see in the screenshot above, the operation returns “Pin removed successfully” in under two seconds. A quick follow-up winget pin list confirms the DirectX entry is gone. No drama, no side effects.

Separating Signal from Noise

This episode is a good illustration that WinGet isn’t infallible. Sometimes its catalog or tooling leaves artifacts behind that look alarming but turn out to be harmless. The DirectX pin on Flo6 was exactly that: a breadcrumb left by WinGet’s own error-handling logic, not by anything I did. A single one-liner clears it up in seconds. Now, winget pin list shows only packages I actually chose to pin. That is exactly how it should be, and I am glad to have one less mystery on my machine. That counts as a win, here in Windows-World. Cheers!

Facebooklinkedin
Facebooklinkedin

In-app Update Beats Remove/Replace

Running WinGet just now on my Flo6 desktop, I got reminded that installer changes sometimes stymie its update facilities. If you look at the lead-in graphic, you’ll see that one upgrade gets blocked because of “different install technology.” Winget goes onto recommend “Uninstall each package, then install the newer version.” Not so fast: IMO, an in-app update beats remove/replace when that’s an option. I’ll explain, and use the Edge browser as an illustration.

You can jump to Edge, click the ellipsis, and get to Help and feedback in 3 clicks. Uninstall/reinstall takes 20+ keystrokes, and might fail.

Why Say: In-app Update Beats Remove/Replace?

My explanation boils down to: less time and effort, fewer keystrokes involved. Jumping to Edge, clicking the ellipsis for Settings, then visiting Help and Feedback to prompt the update process takes 3 mouse clicks (add one more click to restart, and the update is done). Uninstalling, then re-installing edge takes at least 20 keystrokes (“winget uninstall edge”). Worse, it then falls victim to exit code 93. TLDR version: Edge is considered a Windows built-in feature, so it blocks its own uninstall by default.

Sure, you can work around this. And it works for other browsers as directed for Chrome, Firefox, and so forth. But my preferred approach for browsers in particular is: try the built-in update mechanism first, if WinGet steers around an update. It usually does so for a good reason, as is the case here with Edge.

Here in Windows-World, it pays to recognize such cul-de-sacs when they pop up. It saves you the time involved in driving to the end, turning around, and doing something else. Not an unfamiliar experience for Windows warriors, but one best avoided when possible!

Facebooklinkedin
Facebooklinkedin

Post Patch Tuesday Secure Boot Cleanup

September’s Patch Tuesday landed on 9/8. And it brought more than the usual security fixes. KB5124008 and KB5124012 quietly expanded device targeting for Microsoft’s ongoing Secure Boot trust chain. If you haven’t verified your machines yet, now is the time. Secure Boot cleanup is not optional — it is essential maintenance for every managed Windows environment. Indeed, I’d argue that a routine post Patch Tuesday Secure Boot checkup is part of a “new normal” for Windows, with a cleanup to follow if needed.

Why Do a Post Patch Tuesday Secure Boot Check?

Here is the backstory. The old Microsoft UEFI CA certificates that were issued back in 2011, expired in June 2026. Microsoft has been rolling out replacement 2023 certificates through Windows Update for months. September’s updates expanded that rollout further.

KB5124008 and KB5124012 added more “high confidence” device targeting data. That means more PCs are now eligible to receive the new certs automatically. However, some devices still fall through the cracks.

Don’t panic. Devices that haven’t received the new certificates will still boot. Standard Windows updates will still install. But the clock is ticking. A second major deadline arrives in October 2026. You don’t want to be scrambling then.

Why It Matters

Devices that miss the Secure Boot cleanup lose future boot-level security protections. Over time, they become progressively more exposed to boot-level threats. These are the kind that load before Windows even starts. Also, BitLocker and device encryption may break on out-of-synch systems. That means recovery key prompts, startup hangs, and frustrated users calling the help desk.

Running the Garlin Remediation

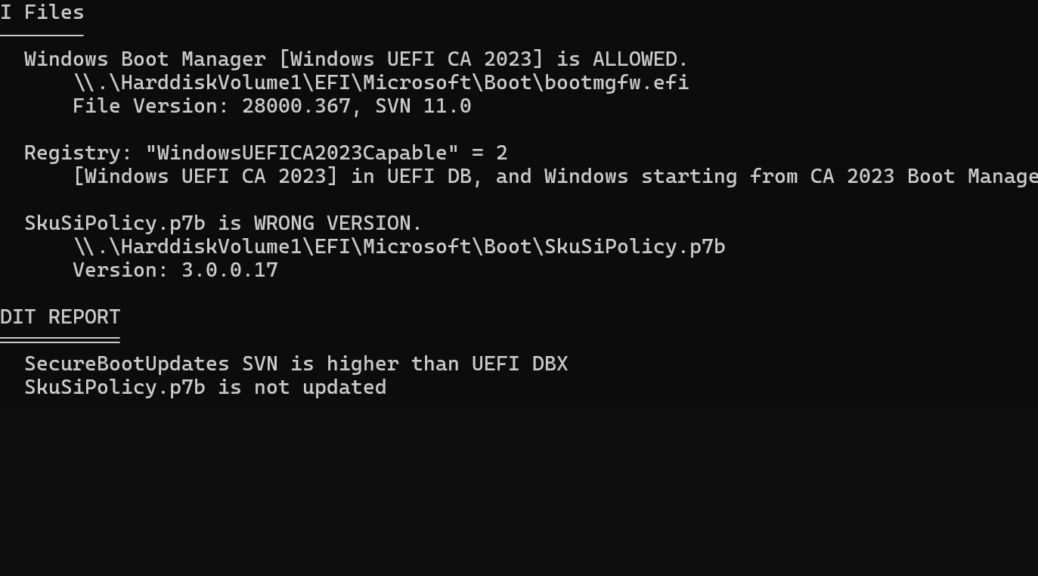
Garlin is a long-time, high-status (and value) member of the online community for ElevenForum.com. He’s been stewarding a long-running thread (now at 188 pages) entitled “garlin’s PowerShell scripts for updating Secure Boot CA 2023” since January 2025. He’s got scripts to handle certificate synch-ups, with all the related DB and DBX fixes to boot (pun intended). Just remember to visit his GitHub site regularly to download the latest ZIP file with scripts to match (his latest update on 9/8 handles the newest Patch Tuesday updates).

As you can see in the lead-in screenshot, after the update Windows incremented SkuSiPolicy.p7b from version 3.0.0.17 to 3.0.0.18. It also updates the Secure Version Variable (SVN) stored in NVM in firmware as part of Secure Boot’s DBX values. After the OS update, certain operations are need to catch the UEFI up with the OS.

Actual Remediation : SkuSiPolicy.p7b

The SkuSiPolicy.p7b value governs which Windows editions (aka “SKUs” such as Home, Pro, Education, etc.) that Secure Boot regards as trusted and bootable. If the policy in the OS and the policy in a boot structure (whether in EFI, on disk, or on bootable media) don’t match, you get “Secure Boot Violation” when you try to boot and nothing more. Not good!

No worries. Garlin’s got a fix for that. If you run his latest Update UEFI script with the right argument it will fix it for you (reboot required). Here’s the syntax:

Update_UEFI-CA2023.ps1 -SkuSiPolicy

If you’re running this in an admin PowerShell session, prepend “.\” (period-backslash) to get it to run. Tip: if you unblock the ZIP file after downloading it from GitHub, the archive’s content will also be unblocked. Otherwise, you’ll end up unblocking them piecemeal. I speak from direct experience on this…

Actual Remediation: SVN

The Secure Version Number (acronym: SVN) is a monotonically increasing integer value also stored in the UEFI DBX value. It provides anti-rollback enforcement. When a bootloader or boot manager tries to loan, UEFI checks its built-in SVN against the minimum SVN stored in firmware. If the boot agent SVN is lower than what’s in UEFI, UEFI won’t load it. Here again, it’s necessary for what’s in the OS and what in the bootloader to agree. After an update (like Patch Tuesday) remediation may be needed.

Here’s what that looks like in PowerShell (admin):

manage-bde -Protectors -Disable C: -RebootCount 1


reg add HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Control\Secureboot /v AvailableUpdates /t REG_DWORD /d 0x200 /f


powershell Start-ScheduledTask -TaskName "\Microsoft\Windows\PI\Secure-Boot-Update"

The first line turns off BitLocker for the next boot to avoid key lookup and entry. It’s only needed for PCs whose C: drive is BitLocker protected. The next line adds a registry key to define and schedule a Secure Boot update task to update the SVN. The third line calls powershell to run that scheduled task immediately. All this stuff shows up in the output of the Garlin check script if you run it properly, so you can copy it from there, right inside PowerShell.

Here’s that syntax:
check_uEFI-CA2023.ps1 -verbose -audit

Don’t forget to prepend the “.\” (period backslash) to run it in PS.

Also: Boot Media Needs Catchup, Too

Here is a step that many admins overlook. Your Windows installation USB drives and WinPE recovery media also need attention. For sure, any media created before January 2025 won’t include the new 2023 Secure Boot certificates. I’ve gotten in the habit of rebuilding boot media each time that SkuSiPolicy.p7b or the SVN increments myself.

What happens if you don’t build new boot media? They may fail to launch on a fully updated machine. Rebuild everything from the latest Windows ADK, MCT (Media Creation Tool), or a current Windows ISO. Then test the rebuilt media on at least one device before you rely on it to get something done.

Run through this quick checklist before you close this task out:

  • ☑ Rebuild WinPE USB from the latest ADK
  • ☑ Rebuild Windows installation USB from a current ISO
  • ☑ Update MDT and WDS boot images if applicable
  • ☑ Test rebuilt media on a pilot device before wide deployment
  • ☑ Document any devices that cannot update (unsupported hardware) as formal exceptions

This is a new and interesting wrinkle on dealing with Windows Updates, especially around the Patch Tuesday milestone. Here in Windows-World such wrinkles accumulate. Don’t let them put your PCs and boot media in peril. Do the necessary, please!

Facebooklinkedin
Facebooklinkedin

Fixing False Vantage Update

If you’ve ever dealt with a Lenovo Vantage false update, you know how maddening it gets. That goes double, when every install attempt fails silently and the same ghost package reappears on every subsequent scan. Sigh.

But that’s precisely what happened to me on a Lenovo ThinkStation P3 Ultra Gen 2 (Arrow Lake-S desktop). There, Lenovo Vantage’s System Update panel stubbornly flagged Intel Dynamic Tuning Technology (DTT) Driver version 9.1.10001.173 as a required update, even after reporting a successful install on the previous try. Sigh again.

Why I’m Fixing False Vantage Update

Here’s the wrinkle: DTT is a laptop-exclusive power-management feature. It’s tightly coupled to Intel’s thermal sensor bus. Specifically, it applies to SWC\VID8086_DTT_* ACPI devices. Alas desktop platforms don’t sport them. My ThinkStation doesn’t have one. It never will. Yet Vantage keeps insisting otherwise.

Furthermore, every install attempt failed without so much as an error dialog. Vantage just re-offered the driver on the very next scan, politely pretending nothing had gone wrong. Time to dig in, and get this thing outtah heah!

Ruling Out the Obvious

First, I tried some obvious remedies. Logging into Vantage directly as Administrator changed nothing. There’s no ellipsis menu, no right-click context option. That means no “suppress this update” checkbox anywhere in the System Update panel. Lenovo simply hasn’t built that in.

Next, I turned to the standalone Lenovo System Update app. After installing the optional Lenovo SoftwareComponent Driver 26.9.0.20 from Windows Update, System Update scanned the machine and correctly reported “No packages applicable.” Clean bill of health. Meanwhile, Vantage still flagged the DTT driver for update. Sigh one more time.

However, that discrepancy was actually useful. It proved the issue lived entirely inside Vantage itself. It’s an artifact of its System Update addin, not  Lenovo’s underlying package catalog. The two tools evaluate the same catalog through completely different pipelines. Importantly, only one of them is wrong.

Tracing That False Positive…

With the obvious paths ruled out, I dug into Vantage’s session data folder:
C:\ProgramData\Lenovo\Vantage\AddinData\
LenovoSystemUpdateAddin\session\
.

Inside, I found two SQLite databases: update_history.db (Vantage’s live working store, rewritten on every scan) and editable_update_history.db (which appears designed to accept external edits). I tried setting the DTT entry status to NotApplicable in the editable_update_history.db. Alas, nothing changed on screen. Vantage reads update_history.db for all rendering decisions and overwrites it with Applicable again after each rescan. The “editable” database, it turns out, is a red herring.

I also found available_updates.json.It’s a 5 KB file that’s rewritten upon each update scan. It gave me a fully parsed package definition, including a Dependencies block that pointed me toward the real culprit.

A (Bogus) WildCard in the XML

Vantage caches each package’s raw XML in its own repository subfolder. For this machine, the DTT package XML lives at:

session\Repository\m1dpf015d_p3ultrag2_25h2\m1dpf015d_p3ultrag2_25h2_2_.xml

Inside that XML, the Dependencies/_Bios/Level section contained two machine-type entries: “*” and “S0NKT*”. The S0NKT* pattern correctly targets specific Lenovo laptop lines that carry DTT-capable thermal silicon. That entry belongs there. The “*” wildcard, however, matches every machine type on the planet — including the ThinkStation’s 30J5 machine type. That entry almost certainly doesn’t belong there, and it looks like a straightforward Lenovo catalog error.

Consequently, without the wildcard, Vantage evaluates the ThinkStation’s machine type against S0NKT*, finds no match, and writes NotApplicable to update_history.db automatically on every future scan. No database patching, no registry hacks — just the correct answer from a corrected applicability list.

PowerShell to the Rescue!

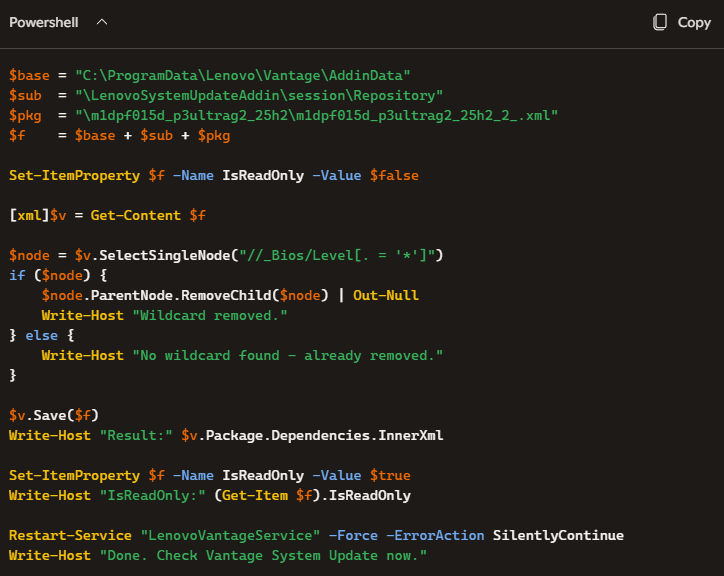
I wrapped the repair into a short PowerShell script called fix_dt.ps1. The logic is straightforward: clear the file’s read-only attribute, load the XML into an XmlDocument object, locate the offending node using an XPath query, remove it, save the file, restore read-only protection, then restart the LenovoVantageService so Vantage picks up the change cleanly.

The lines that do the heavy lifting are (edit to remove line breaks):

$node = $v.SelectSingleNode("//_Bios/Level[. = '*']")
if ($node)
{ $node.ParentNode.RemoveChild($node) | Out-Null }

Setting the file back to read-only afterward is an important step. It prevents Vantage from silently re-downloading a fresh copy of the XML on its next catalog sync and re-introducing the wildcard. Sadly, that would undo the fix entirely.

To run the script, open an elevated PowerShell prompt and execute:

powershell -ExecutionPolicy Bypass -File
"C:\Temp\fix_dt.ps1"

Note: Run this from an elevated (Run as Administrator) PowerShell session. The script must stop and restart the LenovoVantageService, which requires administrator rights. Edit so it runs on one line.

Lessons Learned

This exercise surfaced a few things worth minfing for anyone who’s doing deep Vantage troubleshooting:

  • Vantage and the standalone System Update utility maintain completely separate state databases and catalog evaluation pipelines. Agreement between them is not guaranteed. Disagreement is a useful diagnostic clue, not a dead end.
  • The “editable” SQLite database is a red herring for display suppression. Vantage ignores it when rendering the System Update panel. Don’t waste time on this.
  • A single bogus wildcard in a machine-type applicability list causes a laptop-only driver to haunt a desktop indefinitely. The fix is in the XML, not in the database.
  • When the official UI offers no suppress or hide option for a persistently wrong update, the XML repository is the right lever to pull. Appearances aside, it’s not the SQLite layer above it at fault.

Ultimately, this is a reminder that catalog quality control matters. One stray “*” in a dependency block can send thousands of ThinkStation owners chasing a ghost driver that will never install. If you’ve hit the same Lenovo Vantage false update on a different ThinkStation model, or if you’ve spotted a similar wildcard problem in another Vantage package XML, please drop a comment here. I’d love to know how broadly this catalog bug extends beyond the P3 Ultra Gen 2.

Here in Windows-World, updates sometimes get weird. This time, for once in a blue moon, it’s not WU that’s the culprit. It’s Lenovo. That makes me oddly glad. Go figure!

Facebooklinkedin
Facebooklinkedin