Category Archives: Thoughts & concerns

Looks Like USB4 = PC Bandwidth Backbone

With all the new PC architectures proliferating, I’m thinking about the future role of the USB-C port. I see interesting stuff in NVIDIA RTX Spark, GoogleBook, post-Copilot+ PCs (especially Snapdragon X2) and top-of-the-line X64 AMD and Intel boxes. Especially, it looks like USB4 = PC bandwidth backbone for externals going forward. Let me explain…

Why Assert USB4 = PC Bandwidth Backbone?

USB is the central nervous system for personal computing. Most keyboards, drives, displays, and docks eventually trace back to this standard. USB4 Version 2.0 raises its bidirectional bandwidth ceiling to 80 Gbps. A single USB-C cable now handles data, video, and up to 240 W of power. That combination isn’t incremental, it’s more. The whole PC peripheral ecosystem is being rebuilt around USB4, and IT professionals need to understand what that means today.

The Big 5 External Device Categories

USB now dominates five distinct external device categories. Each one benefits directly from the 80 Gbps headroom that USB4 v2 provides. Here are the five categories driving that shift:

  • External storage: NVMe SSDs, traditional HDDs, and USB flash drives all benefit from faster sustained throughput and lower latency over USB4 v2 links.
  • Displays and docking stations: DisplayPort 2.1 tunneling over USB4 v2 enables multi-monitor 8K setups and single-cable desk configurations.
  • Networking adapters: USB4 v2 makes 2.5 GbE and 10 GbE Ethernet adapters practical for home labs, creative workstations, and remote offices.
  • Peripherals: Keyboards, mice, webcams, audio interfaces, and MIDI controllers all connect reliably with lower latency and higher headroom than before.
  • External GPUs and compute accelerators: The newest category, enabled by PCIe Gen4 tunneling over USB4 v2, opens the door to external graphics and AI inference workloads.

USB4 External Storage: Real-World Speed

USB4 v2 enables external NVMe SSDs to reach up to 3,800 MB per second in sequential read speeds. That figure rivals many internal M.2 drives installed directly on the motherboard. PCIe Gen4 tunneling over the 80 Gbps link makes this possible. The tunnel carries four lanes of Gen4 PCIe traffic inside the USB4 protocol stack. Earlier USB4 v1 devices topped out around 2,000 MB per second under real-world conditions. Version 2 represents a meaningful and measurable leap. For video editors ingesting 4K or 8K footage, the difference is felt immediately. A 1 TB file transfer that once took ten minutes now completes in roughly five.

Displays and Docking Stations

DisplayPort 2.1 tunneling over USB4 v2 supports dual 8K displays at 60 Hz. A single 12K display is also within reach for demanding visualization workflows. The asymmetric bandwidth mode pushes 120 Gbps in the display direction. That frees up the remaining 40 Gbps for simultaneous data and peripheral traffic. A single cable dock can now replace a tangled collection of adapters and separate power bricks. USB Power Delivery 3.1 adds up to 240 W of charging capacity through the same cable. A 16-inch laptop with a discrete GPU charges fully through the dock connection. For IT departments standardizing workstation setups, the cable reduction alone justifies the upgrade.

External Networking and Peripherals

USB4 v2 makes 10 GbE Ethernet adapters a practical upgrade for home labs and creative workstations. The bandwidth headroom is sufficient to sustain full 10 Gbps network throughput alongside active display and storage connections. Webcams, audio interfaces, and MIDI controllers all benefit from lower latency and higher sustainable throughput. A USB audio interface running at 192 kHz with low buffer sizes is far more stable over USB4 v2 than over older USB 3.2 connections. USB4 v2 also maintains backward compatibility with USB 3.x and USB 2.0 devices. Existing peripheral investments are protected. Nothing on your current desk becomes obsolete when you move to a USB4 v2 host.

Why Thunderbolt 5/USB5 Faces an Uphill Road

Thunderbolt 5 sits atop the USB4 v2 physical layer. It delivers the same 80 Gbps bidirectional bandwidth with stricter mandatory certification requirements. That certification is Intel-controlled, and it adds cost to both host silicon and peripheral hardware. Most Windows OEMs are shipping USB4 v2 ports labeled simply as “USB 80 Gbps,” without full Thunderbolt 5 certification.

Indeed, AMD platforms have broadly adopted USB4 v2 across their Ryzen and EPYC product lines. The installed base of USB-compatible devices vastly outnumbers the catalog of TB5-certified accessories. For most enterprise and prosumer buyers, USB4 v2 is the practical mainstream choice today. Thunderbolt 5 remains the right answer when maximum certified performance and guaranteed interoperability are required. Both standards deserve consideration. They are not adversaries; they share the same physical foundation.

Looking Ahead: USB5/Getting Past 80 Gbps

USB5 is not yet finalized as of late 2026. The USB Implementers Forum is actively working on specifications that could reach 120 Gbps or higher. Realistic consumer hardware availability is unlikely before 2028 or 2029. Silicon development cycles, platform integration, and ecosystem buildout all take time. Plus, Gen 5 tunneling remains an open issue.

Thus, Thunderbolt 5 is likely to remain the top certified performance ceiling through at least 2027. That makes USB4 v2 the right infrastructure investment right now. Cables, docks, enclosures, and adapters purchased today will carry forward into USB5-era systems. Building on USB4 v2 now means you are not starting over when the next generation arrives.

That’s Why USB4 Is THE Bandwidth Backbone

USB4 v2 at 80 Gbps now handles storage, displays, networking, peripherals, and power from a single port and a single cable. All five of the Big 5 external device categories are well-served at this bandwidth tier. This is not a niche technology for early adopters. It is the connective tissue of the modern PC, shipping in mainstream laptops, desktops, and docking stations from every major OEM. The gap between USB4 v2 capability and USB 3.2 era infrastructure is real and growing.

Here is a call to action: audit your current ports and cables this week. Identify every system still running USB 3.2 Gen 2 or older Thunderbolt 3 connections. Prioritize USB4 v2 or Thunderbolt 5 ports at your next system refresh. The bandwidth backbone is already here. Make sure your infrastructure is built on it. Cost and availability appear to put USB4 as “king of the hill” for the next 3-5 years. Let’s see how it turns out, shall we?

Facebooklinkedin
Facebooklinkedin

Can Googlebook Occupy a Real Niche in the Computing Landscape?

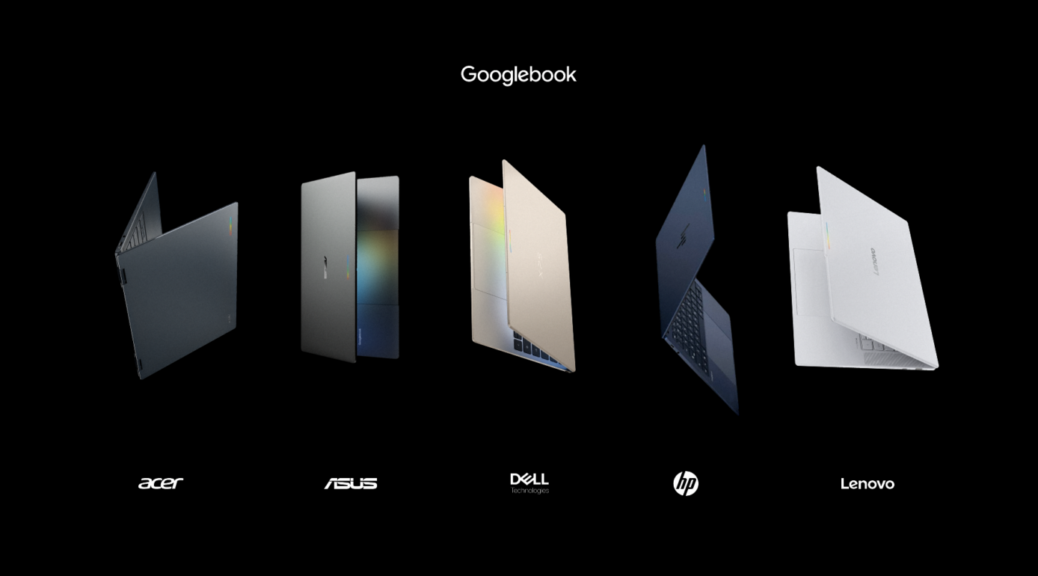
Today, September 21, Google fired off its Googlebook platform. Five tier-one OEMs (namely, ASUS, Acer, Dell, HP and Lenovo) are all launching “premium” laptops into this newly defined space. Thus, asking “Can Googlebooks occupy a real niche” is a serious question. On the one hand the computing landscape is already carved into deeply entrenched players. On the other, that carving leaves gaps, and Google is betting it has found one it can occupy, and prosper from.

Who Already Occupies the Landscape?

Each major platform has staked out its territory clearly. Windows dominates business, enterprise, and line-of-business applications. It owns Active Directory, Microsoft 365, and decades of legacy software compatibility. That’s an enormous moat to cross.

Apple Silicon Macs own creative professionals and developers. Xcode, Final Cut Pro, and Logic Pro anchor a loyal, high-spending ecosystem. ChromeOS owns the education budget tier, shipping hundreds of millions of units into classrooms globally. Linux serves the hardcore developer and sysadmin community (and runs on 75+% of global Web and enterprise servers) with precision and flexibility.

Each of these niches is deeply entrenched. Therefore, the question is serious: does Googlebook find a gap, or does it create a new one? Those are very different challenges, and only one of them is easy.

Can Googlebook Occupy a Real Niche Amidst 3B Android Carriers?

This is Google’s best proposition. There are roughly 3 billion active Android devices globally. Most of their users have never found a laptop that felt native to this ecosystem. That’s a genuinely underserved market, and Google knows it.

Googlebook OS merges Android’s app stack with ChromeOS foundations. It adds phone-to-laptop handoff via “Continue On” and “Cast My Apps.” These features mirror Apple Handoff and iPhone Mirroring directly. In short, Google is attacking Apple’s continuity story head-on.

PCMag’s Brian Westover is cautiously optimistic. He called Googlebook “Google’s biggest hardware gamble to date,” but added that he is “betting on Google to reinvent the laptop again” (PCMag). He also noted: “This is probably the worst version of the Googlebook, it only gets better from here” (PCMag). The Android continuity story is real. Even so, it has to work, and not just in demos.

What Do Experts Say? Pros and Cons

Not everyone is convinced. Oflight’s enterprise analysis is frank: “Real-world software compatibility and platform stability will only be provable after the fall 2026 launch. Early adoption carries meaningful validation risk” (Oflight). That’s an outright caution for would-be enterprise buyers.

Consider further that Google’s hardware track record is mixed. The Pixelbook line is dead. Stadia is gone. Pixel Slate never took off. Enterprise buyers have long memories, and Google’s history of platform abandonment is a nagging concern.

On the upside, Oflight also notes that Googlebook inherits Chromebook’s low IT management overhead. It runs on the same Google Admin Console. For schools and SMBs already using Google Workspace, the upgrade path is smooth and familiar (Oflight).

PCWorld’s Ben Patterson frames the AI divide well. He describes it as “NVIDIA RTX Spark, which delivers local AI, versus Google Gemini Spark, which bets on the cloud” (PCWorld). Googlebook bets the cloud. RTX Spark bets local compute. Both bets make sense, but both can’t win (though both can lose).

NVIDA RTX Spark Arrives Oct 7

Mark October 7, 2026 on your calendar. That’s when NVIDIA’s RTX Spark platform hits. RTX Spark is a serious high-end play: up to 128 GB unified memory, 6,144 Blackwell CUDA cores, and 1 petaflop of FP4 AI performance. Pricing runs $2,000 to $3,500 and up.

RTX Spark doesn’t compete with Googlebook directly. However, it does apply real pressure at the top of Googlebook’s $899-to-$1,299 range. A buyer at $1,299 could pause. For $700 more, RTX Spark delivers local AI processing with full Windows app compatibility. That’s a considerable counter-offer.

Gzmato’s TCO analysis finds only 5 to 10 percent of buyers truly need that kind of comuting power (Gzmato). But that buyer group includes developers, researchers, and AI pros. Those are the very users Googlebook is trying to recruit. PCWorld’s Patterson captured it cleanly: “2026 is shaping up to be [NVIDIA] Spark versus [Gemini] Spark, and only time will tell” (PCWorld).

Rating Googlebook’s Odds of Success

Where does this leave Googlebook? The following table scores some key factors. Note further that strength alone does not guarantee a niche. Execution, timing, and staying power all matter. Google must prove it will not abandon this platform the way it abandoned others.

Factor Assessment
Android ecosystem leverage Strong: 3B+ active devices and a vast Play Store
OS credibility at launch Unproven: validation risk is real
AI feature differentiation Solid, but cloud-dependent vs. RTX Spark’s local story
Price positioning Competitive vs. MacBook; exposed vs. RTX Spark
OEM commitment Genuine: 5 tier-1 partners is no soft launch
Google’s staying power The biggest wildcard, given previous history

The niche is real but not yet earned. Android users without a native laptop have nowhere good to go right now. That is a genuine market. And it’s way larger than any hardware niche Google has targeted before. Alas, the computing landscape does not reward goodwill: It rewards execution.

Googlebook ships today, October 4. RTX Spark ships October 7. The next six months of reviews, compatibility reports, and developer adoption will answer the question analysts can’t answer today. Can Googlebook occupy a real niche in the computing landscape, or will it become another chapter in Google’s long list of hardware near-misses? Lots of people will be watching closely, including yours truly. I’ll also be wondering if this could pose a real challenge to Windows-World, given my own focus and interests. We’ll see!

Facebooklinkedin
Facebooklinkedin

FAT32 UFD Nixes “Repair My PC”

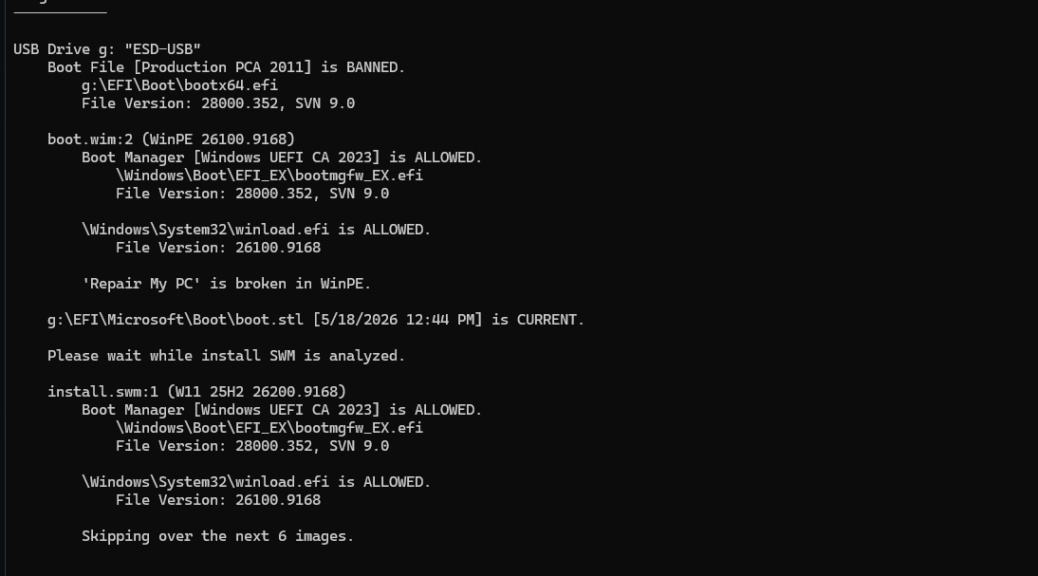
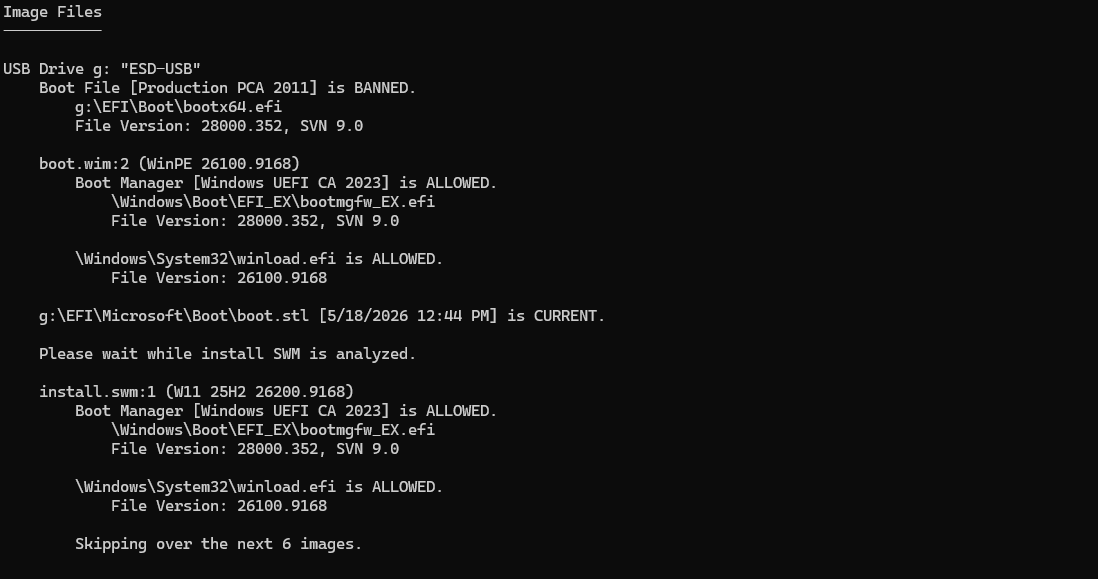
Here’s an interesting one. I tried out the latest Garlin scripts this morning (dated 8/24). The boot media check turned up something new. It reported that a new Windows 11 facility wouldn’t run from my MCT-based Windows installer UFD. And indeed, upon investigation, it turns out that using a FAT32 UFD nixes “Repair my PC” capabilities in WinPE. But that’s for a good and understandable reason, as I’ll explain.

TLDR version: Boot an MCT-generated Windows 11 setup USB and click “Repair your computer.” On many FAT32-formatted drives, including these, nothing happens. That option is simply broken. Here is why, and what you can do about it.

Why FAT32 UFD Nixes “Repair My PC”

Windows 11 setup media built with the Media Creation Tool on a FAT32 drive hits a hard wall. FAT32 caps individual file sizes at 4 GB. A Windows 11 install image blows past that ceiling.

Microsoft’s solution is to split the image into two files named install.swm and install2.swm(swm is, of course, a “split WIM file” ICYDK). On the drive I examined, that pair totaled about 5.6 GB compressed. Setup.exe handles this format just fine during installation. The problem surfaces elsewhere.

WinPE Can’t Find (or Handle) the Source

Clicking “Repair your computer” in the Setup UI triggers a search. The WinPE environment in boot.wim looks for install.wim or install.esd in the sources folder. Neither file exists on a FAT32 UFD.

Only install.swm and install2.swm are present. WinPE recovery tools cannot enumerate split WIM files for repair operations. They expect a single, monolithic image file. Without it, the repair chain fails before it starts.

Please note that this is neither a certificate nor a Secure Boot issue. Garlin confirmed that all signing credentials in boot.wim were valid. Strictly speaking, the “broken” label emerges from a missing monolithic image, nothing more.

NTFS Can Fix What’s Broken, But…

The root cause is FAT32. The cure is straightforward: rebuild the drive using NTFS.

Rufus handles this cleanly. Point it at a Windows 11 25H2 ISO, choose NTFS as the file system, and let it run. NTFS has no 4 GB per-file ceiling. A Rufus NTFS build produces a single install.wim that WinPE can locate and read without complaint.

Rufus also ships a current, properly signed bootloader. That quietly resolves a secondary Garlin finding as well: a BANNED bootx64.efi signed by the deprecated Production PCA 2011 certificate. On an NTFS Rufus build, that file is replaced automatically.

Practicing Proper WinRE/WinPE Repairs

A FAT32 Windows 11 setup USB remains fully functional for clean installs. The split WIM has no effect on setup.exe. However, the “Repair your computer” path is dead on arrival.

On a machine that refuses to boot, that missing option could matter a great deal. Building setup media on NTFS costs nothing extra. Rufus is free, and a rebuild takes only a few minutes.

For a USB you may need under pressure, a working repair option is worth the small extra effort. That said, I have observed that some PCs (notably, various Lenovo and Toughbook laptops in my custody) simply won’t boot to an NTFS-formatted UFD. That takes “Repair my PC” off those particular tables, for good or ill.

Check It for Yourself

Run Garlin’s check-bootmedia script against your Windows 11 setup drives. If you see ‘Repair My PC’ is broken in WinPE, you now know why that shows up. If you rebuild on NTFS using Rufus with a current ISO, that repair option will be there when you actually need it. But only if your target PC will boot from an NTFS-formatted UFD. That’s why you have to check! Here in Windows-World, it’s best to know such things beforehand.

Note to Microsoft: Maybe you guys should buy or license Rufus so you can quickly jump MCT and “Create a recovery drive” into a completely modern, Secure Boot aware (and friendly) stance. IMO, that’s a good idea, so please give it some thought.

Oho! There’s ANOTHER Garlin Script for That…

Turns out you can download and apply yet another Garlin script to fix this very issue. It’s called Repair_My_BootWIM.ps1. Run it against your offending boot media and the problem gets fixed automagically. It just worked on my test G: drive created from MCT last week. No Rufus needed. Go figure!

Notice the text that reads “‘Repair My PC’ is broken in WinPE.”  no longer appears. Fixed!

Facebooklinkedin
Facebooklinkedin

Windows 10 ESU Gets Another Year

Microsoft has added a year to the expiration date for its Windows 10 Extended Security Updates (ESU) program. This gives consumers, businesses and organizations another year of critical security patches on their Windows 10 devices. In turn, that provides much-needed breathing room for transitioning to Windows 11 or newer platforms, ensuring users remain protected against emerging threats. As Windows 10 ESU gets another year of life, those running Windows 10 get another year to figure out “What’s next?”

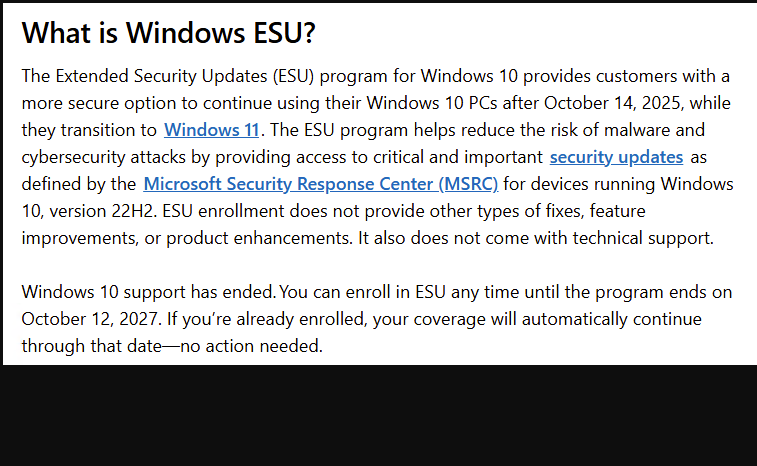
The lead-in graphic for this post shows the MS ESU Explainer that pops up inside that OS when you visit Settings > Update & Security, then click the link that reads “Learn more about Extended Security Updates.” As far as I can tell, MS just extended that date this week. FWIW, other published sources (e.g. WinAero, Windows Latest, Windows Central, etc.) agree.

What Windows 10 ESU Gets Another Year Means

Extended Security Updates (ESU) is a program Microsoft offers to organizations that need to keep Windows 10 systems secure beyond the official end-of-support date. Officially, Windows 10 support ended on October 14, 2025. Even so, ESU allows customers to receive critical and important security updates for some time after that date. This “expiration date” just got extended, as you can see in the lead-in screencap.

This program is especially valuable for businesses with legacy applications or hardware that are not yet compatible with Windows 11. It helps them avoid security risks while they plan and execute their migration strategies.

Why the Extension Matters

The extension of Windows 10 ESU for another year reflects the reality that many organizations face challenges upgrading their infrastructure. Whether due to budget constraints, application compatibility issues, or operational complexities, migrating to a new operating system is rarely straightforward.

By extending ESU, Microsoft acknowledges these hurdles and offers a safety net. This additional year of support means organizations can continue receiving vital security patches, reducing the risk of vulnerabilities that could be exploited by cyber attackers.

What’s Included in the Extended Support?

The ESU program focuses on delivering security updates classified as critical or important by Microsoft. These updates address vulnerabilities that could allow remote code execution, privilege escalation, or denial of service attacks.

However, ESU does not include feature updates or non-security fixes. Organizations still need to plan for a full upgrade to a supported operating system to benefit from new features and improvements.

How to Get Windows 10 ESU

Eligible customers can purchase ESU licenses through Microsoft’s Volume Licensing programs or authorized resellers. The pricing typically increases each year, reflecting the diminishing support window. Individual users may also qualify for ESU, either by activating Windows Backup to sync files and settings via OneDrive, or by redeeming 1,000 MS Reward points.

To activate ESU, organizations must install specific activation keys and ensure their systems are up to date with the latest servicing stack updates. Microsoft provides detailed guidance and tools to help with this process. Individual users typically upgrade directly through WU, without having to reactivate Windows 10 licenses.

Planning Your Migration

While the ESU extension offers more time, it’s not a permanent solution. Users should use this period to accelerate their migration plans to Windows 11 or other supported platforms.

For IT-driven organizations, key steps include:

  • Assessing Compatibility: Evaluate applications and hardware for Windows 11 readiness.
  • Testing: Pilot Windows 11 deployments in controlled environments.
  • Training: Prepare IT staff and end-users for the new operating system.
  • Deployment: Roll out Windows 11 in phases to minimize disruption.

For SOHO and individual users, migration will usually mean disposing of older PCs not able to meet Windows 11 hardware requirements. Replacing those typically involves purchasing a new or used PC or laptop with Windows 11 pre-installed. Optionally, they may (or may not) use a program such as PC Mover to transfer their apps, files, and settings to the new OS.

One Year Adds Time, But Cures No Ills

The additional year for Windows 10 ESU is a welcome relief for many organizations still navigating the complexities of OS migration. It ensures continued protection against security threats while providing a buffer to plan and execute a smooth transition.

However, relying on ESU indefinitely is not advisable. The best strategy is to leverage this extension as a bridge toward a fully supported and modern operating system environment.

By staying informed and proactive, IT teams can safeguard their infrastructure and keep their organizations secure in an ever-evolving threat landscape. Individual consumers gain time to save up for a new PC or laptop, and plan their migration strategy, too.

Facebooklinkedin
Facebooklinkedin

Benefits from Buying One Generation Back

Patience isn’t a virtue many tech shoppers cultivate. But here’s the thing: waiting just one product cycle can put serious money back in your pocket. Buying one generation back is one of the smartest, most underappreciated moves in the PC-buying playbook. You get hardware that was cutting-edge twelve months ago, at prices that make last year’s flagship look like a budget pick.

Case in point: a June 19 Windows Central story entitled “Dell’s stunning XPS 13 drops to under $1,000, packing a massive 32GB of RAM.” Careful reading and a little thought reveals that with the newer, faster, more efficient CPUs now out in the market, a markdown seems the right way to clear out this older inventory.

Why Buying One Generation Back Makes Sense

When a manufacturer ships a new laptop model, retailers have a problem: they’re sitting on inventory of the outgoing model. They need it gone. Fast. So prices drop — sometimes dramatically — to clear shelf space and warehouse stock.

Here’s the kicker: the old hardware didn’t suddenly get worse. The processor that impressed everyone last year still handles your spreadsheets, video calls, and browser tabs just fine. Performance gaps between consecutive generations are usually modest — often 10–15%. That’s not worth full MSRP. But a 25–40% discount? Now we’re talking.

Retailers, manufacturers, and third-party sellers all play this game. The window is finite, though. Once inventory clears, deals disappear.

Real Savings, Real Hardware

Don’t take my word for it. Here are four real examples of what buying one generation back actually looks like in dollar terms:

  • Dell XPS 13 (9345) with Snapdragon X Elite: Dropped from $1,399.99 to $999.99 — that’s a full $400 in savings — after newer XPS models landed on shelves.
  • Dell Inspiron 15 (13th-gen Core i5, 2K touchscreen): Fell from $849.99 to $549.99 at Best Buy — $300 off — as 14th- and 15th-gen Inspirons took over the lineup.
  • HP OmniBook 3 (Snapdragon X, 14-inch, 16 GB RAM): Slid from $949.99 to $549.99 — a whopping $400 discount — following the launch of the updated OmniBook 5 and 7 models.
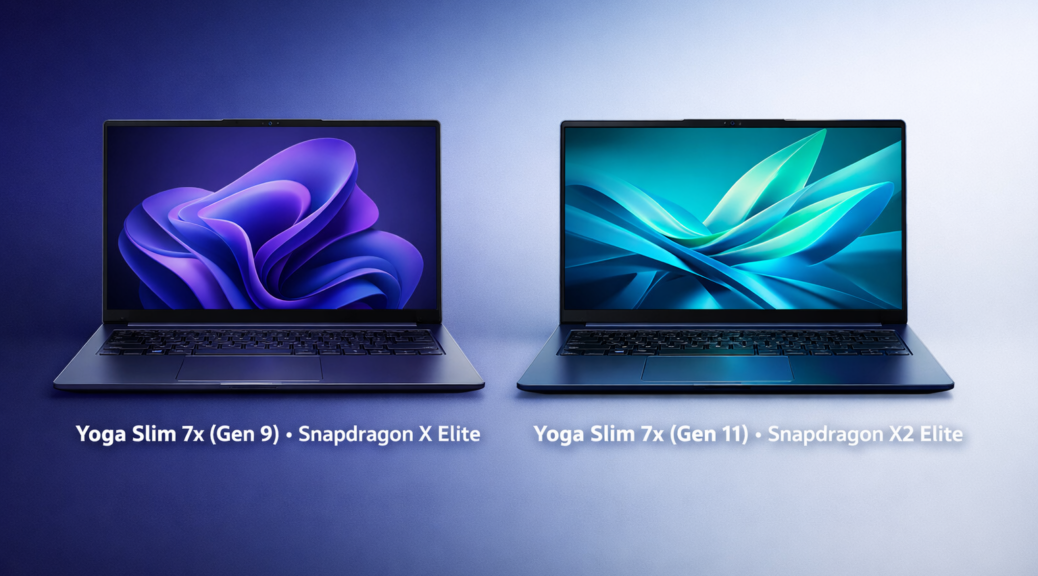
  • Lenovo Yoga Slim 7x (Gen 9, Snapdragon X Elite, 14.5″ 3K OLED): dropped from $1,300 to $800 at Best Buy — a $500 savings — as the 2026 Gen 11 (Snapdragon X2 Elite) arrived to replace it.

Those aren’t rounding errors. That’s real money. On the XPS 13 and Slim 7X alone, you’d save $900 combined. Buy both and you’ve basically gotten one laptop free.

Where to Hunt for Such Deals

You have to know where to look. The best hunting grounds are the Dell or Lenovo Outlet stores, HP’s certified refurbished storefront, and Best Buy’s clearance section (online and in-store). Open-box listings at major etailers are also worth bookmarking.

Timing matters. The best deals on buying one generation back typically surface right when a successor model is formally announced or begins shipping. That’s your signal. Manufacturers and retailers want the old stock gone before the new wave arrives.

Pro Tip

Set price-drop alerts using tools like CamelCamelCamel (for Amazon) or Google Shopping alerts. You’ll catch markdown as they pop up, before the good stuff disappears.

Bookmark those clearance pages right now. Set price alerts on the models you’ve been eyeing. Then act fast when the drop hits. Wny? Because quantities on outgoing inventory are always limited, and once it’s gone, it’s gone. Buying one generation back rewards the prepared shopper, not the hesitant one. A little patience up front means a lot less money out the door at checkout.

Here in Windows-World, we must grab our savings while the discounts persist. He or she who hesitates is lost. Get your budget together and keep you eye on the “new new” PCs, so you can cash in on the “old new” PCs!

Facebooklinkedin
Facebooklinkedin

Evolving Windows Device Security Hardware

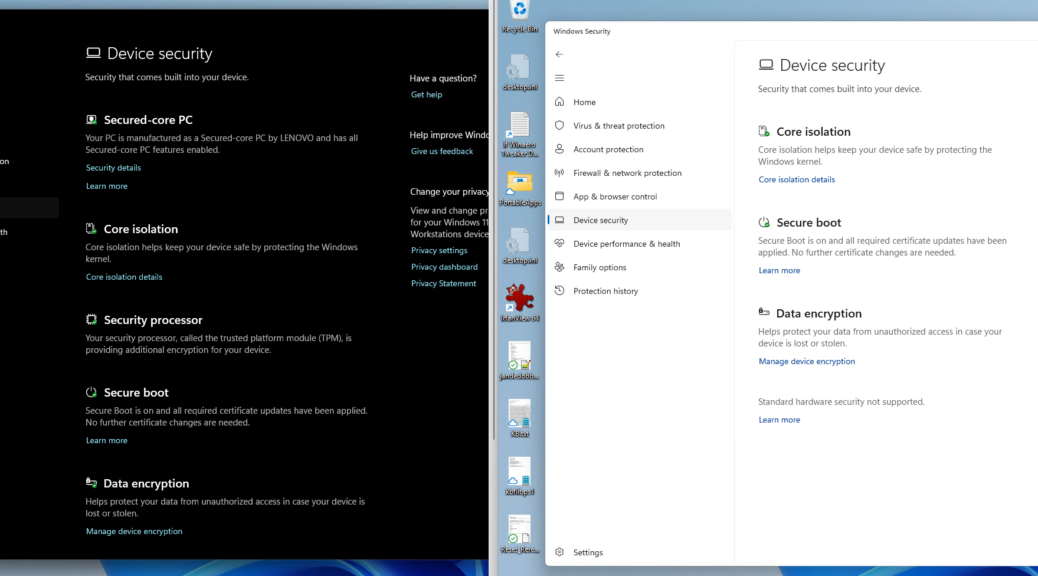
This weekend, I pulled up the Windows Security Device security panel on my ThinkPad P16 Gen 3 (2025 build) and my ThinkPad X380 (2018 build; made a 2017 debut), and put them side by side. The difference showed me something interesting — namely,  evolving Windows Device Security hardware.

Both machines run Windows 11. Both are solid, business-class Lenovo laptops. However, the P16 Gen 3 panel is full: every tile is lit, every checkmark is present. The X380 panel, OTOH, shows obvious gaps. It closes out with a blunt verdict: “Standard hardware security not supported.” The lead-in screenshot tells a story of Windows device security hardware evolution over 7 years.

The X380 isn’t a bad machine. It was just built before the security landscape it now lives in actually existed. That distinction matters, so it’s worth unpacking what’s missing and why.

What Evolving Windows Device Security Hardware Means

The most visible absence on the X380 is the Secured-core PC badge. Not surprising when you check the timing: MS launched the Secured-core PC initiative on October 21, 2019. That’s over a year after the X380 shipped. The X380’s 8th-generation Intel Core (Kaby Lake Refresh) silicon predates the Dynamic Root of Trust for Measurement (DRTM) and System Guard Secure Launch capabilities that Secured-core status requires.

In sharp contrast, the P16 Gen 3 runs Intel Core Ultra 9 silicon that fully implements Intel Hardware Shield. That’s what underpins DRTM and Kernel DMA Protection at the hardware level. In addition, Secured-core mandates HVCI (Hypervisor-Protected Code Integrity) enforced at the silicon level. Older CPUs can enable this in software. Alas, they cannot deliver the hardware-based capability that Microsoft’s Secured-core PC requirements demand.

The second gap is the Security processor tile. The P16 Gen 3 surfaces an explicit tile confirming that TPM is visible, active, and reports correctly to the Windows Security layer. The X380 does have a TPM  (Lenovo shipped TPM chips on all commercial machines by 2017). However, Windows Security on the X380 doesn’t surface that tile. Its firmware TPM integration doesn’t offer stricter attestation-visibility that newer UEFI and firmware stacks expose to the operating system. The chip is there, but the trust handshake simply isn’t good enough for Windows to show it as an attestable asset.

The X380 Bottom Line Is…Not Quite There

That brings us to the X380 bottom-line verdict: “Standard hardware security not supported.” Windows delivers this message when a device cannot simultaneously confirm TPM 2.0 attestation, Kernel DMA Protection, and VBS readiness at the hardware level. The X380 can satisfy some of those requirements individually, but not in hardware. As a result, it falls short of the full baseline. That is not a misconfiguration, but falls out because the required silicon-to-firmware-to-OS trust chain simply wasn’t designed into the X380.

What Both Machines Get Right

Let’s be fair to the X380, because calling it obsolete would be wrong. Core isolation runs. And indeed, Virtualization Based Security operates in software mode. Secure Boot is fully active, with all certificates up to date. BitLocker encrypts the drive. These are the foundational Windows security capabilities that survive on older hardware, and they aren’t trivial. The X380 still protects data at rest and guards boot integrity against tampering. It simply cannot make the firmware-to-OS trust chain guarantees that silicon-rooted security delivers. There’s a meaningful difference between those two tiers, but the lower tier is not nugatory.

A Seven-Year Gap in Numbers

Between 2017 and 2025, Intel moved from 8th-generation Kaby Lake Refresh to Core Ultra (Meteor Lake and Arrow Lake). AMD traveled from Ryzen 1000-series to Ryzen AI 300. Along the way, Microsoft introduced Secured-core PC certification (2019), Windows 11’s hard TPM 2.0 requirement (2021), the Pluton security processor co-design with AMD and Intel (2022 ), plus evolving memory encryption standards. Thus, the Device Security panel on a 2025 machine doesn’t just reflect software updates . It also reflects seven years of deliberate co-design among Microsoft, Intel, AMD, and various OEMs, baked directly into the silicon and firmware before the OS even loads.

Wondering About Continued Viability?

If you’re running a 2017/8-era machine and wondering why your Device Security panel looks thin, it’s not your fault and it’s not your settings. It’s the silicon that falls short. The hardware security stack that Windows 11 fully expects is built into CPU microarchitecture and firmware design from 2019 onward. No amount of registry tweaking can close that gap. That said, your older machine isn’t broken. Instead it’s working at a lower tier of the trust hierarchy, but it still does real security work. When it is finally time to refresh, pull up the Device Security panel on your new, Secured-core PC. It  fills those gaps, and offers more and  better security capability. Worth it!

Facebooklinkedin
Facebooklinkedin

Sandbox Effect Keeps Spreading

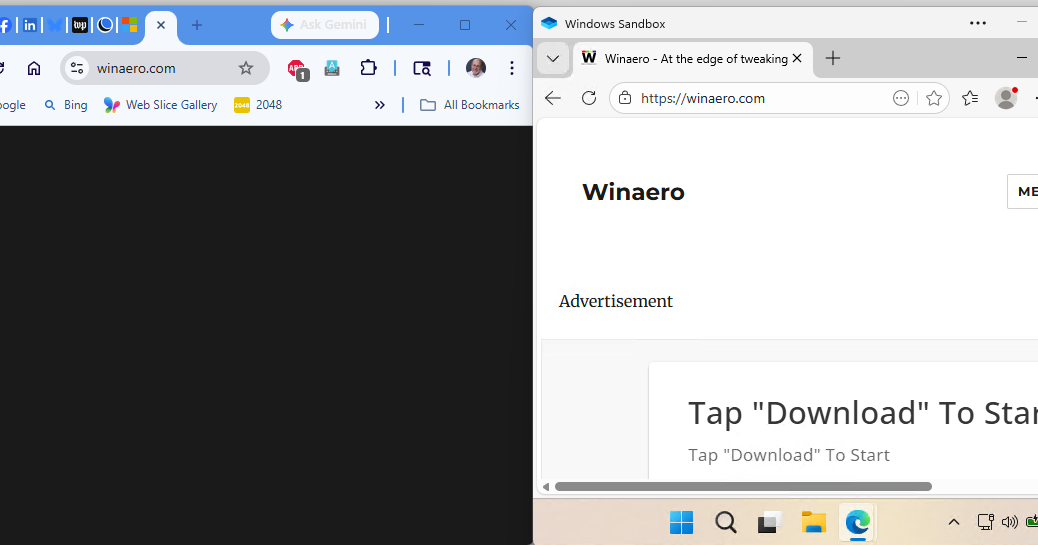
OK, I admit it. I run Adblocking software inside my web browsers. To see web pages nowadays, that means I bump them up to 150% so I can read the text. That leaves less room for other stuff, especially ads. But I’ve noticed that an increasing number of websites simply won’t let viewers visit unless those visitors permit the ads to show. So I open those sites inside Windows Sandbox because it works as a no-filters and no-blocks-applied environment. Alas, this “Sandbox effect” keeps spreading as more and more sites make me do this.

Why Say: Sandbox Effect Keeps Spreading

I got a particularly rude wake-up call about this on Wednesday. In fact, I didn’t even figure it out until this morning. Two days ago, I noticed that WinAero was coming up in Firefox (where it’s in my favorites) as an all-back page. I even asked Copilot what might be wrong and it speculated that something with the CDN (Content Distribution Network — e.g. Akamai, etc.) might be wonky.

Wrong. This morning, it dawned on me that this “black screen” might be a particularly draconian implementation of a “no ad blocking” policy. And indeed, that’s what it appears to be (lead-in graphic, left). When I open the same site in Windows Sandbox (lead-in graphic, right) it comes up in readable form right away. Wowie-Zowie.

The Sandbox List Is Growing

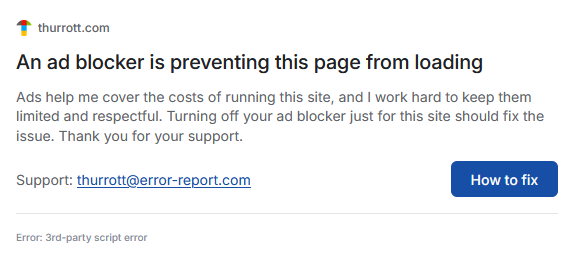
Minutes ago, I had a similar experience at Thurrott.com. I suppose I should be grateful, because that site operator at least had the courtesy to tell me what was going on. Here’s what it showed me after a click-through from a “problem loading the page” error message:

Life is interesting when one is inclined to appreciate being informed that they must watch ads on a website, or skedaddle. Here in Windows-World, gratitude often takes unusual forms. This one, methinks, is more unusual than most. Happy Friday!

Facebooklinkedin
Facebooklinkedin

Why Switch One 2020 Mobo for Another?

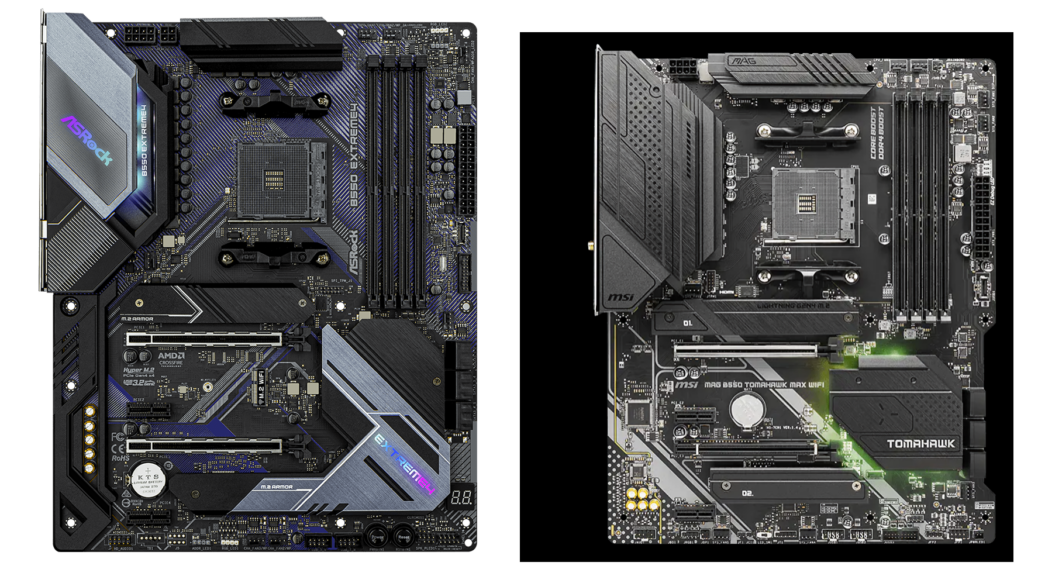
I’m surprised. I’m actually considering replacing a 6-year-old Asrock motherboard with an MSI of the same age. Basically, I’ve gotten tired of fighting UEFI and firmware issues on the Asrock that serves as the foundation for my production desktop. I see reviews and other online evidence that the MSI MAG B550 Tomahawk Max will solve those problems. It costs US$150, which is a relatively small sum when compared to the days and days I’ve spend fighting with the Asrock board in the last month.

Why Not Switch One 2020 Mobo for Another?

I’m pretty sure I can take Flo6 apart, swap mobos, and get back up and running in an afternoon. I’ve almost had to take the whole thing apart half-a-dozen times recently to pull the GPU, various drives (including the primary SSD), and the CMOS battery. Why not go all the way?

Simply put: I don’t feel like funding a complete rebuild into a new system right now, given prevailing costs for RAM and SSDs. I can make this switch for another US$150, versus US$2,650 for a similarly equipped i714700K based build.

That’ll have to wait for the general exchequer to charge up a bit. Maybe next year? For now, I’ll be happy to get a system that boots properly, and handles Secure Boot without major issues. Let’s see what happens, shall we? I’m giving it a try…

Facebooklinkedin
Facebooklinkedin

Secure Boot Oddities Accumulate

Although I’m resigned to living without secure boot on the B550-based desktops here at Chez Tittel, that doesn’t stop me from trying other fixes from time to time. Indeed, I discovered a great thread about secure boot keys at ElevenForum, and learned more about what’s going on under the hood. Along the way, I gave myself a terrific scare as I saw more secure boot oddities accumulate. Here’s what happened…

Registry Key Change Helps Secure Boot Oddities Accumulate

One must provide Windows with a a couple of instrux to ask the OS to update secure boot key certificates, to wit:

Set-ItemProperty -Path “HKLM:\SYSTEM\CurrentControlSet\Control\SecureBoot” -Name “AvailableUpdates” -Value 0x40

Start-ScheduledTask -TaskName “\Microsoft\Windows\PI\Secure-Boot-Update”

One is then instructed to reboot Windows twice to get those instructions to work as they’re intended to. What it doesn’t say is that strange things might happen before the first reboot occurs.

Black Screen, No UEFI — No Nothin!

I about had heart failure when I rebooted my PC this morning and the Flo6 came up black with no normal boot sequence. No Asrock logo, no instructions to hit Del or F1 to load EFI, no F11 for boot menu. There’s not much one can do to fix a Windows PC that won’t do anything, short of taking it into a shop.

So I turned off the power supply, then hit the power button for 10 seconds to make sure all the capacitors got discharged. Then I took a break and walked away from the machine for 10 minutes. Then I powered on again. Phew! This time, the Asrock logo appeared, and it booted into Windows 11.  To my great relief, the second reboot was no big deal, and I was glad.

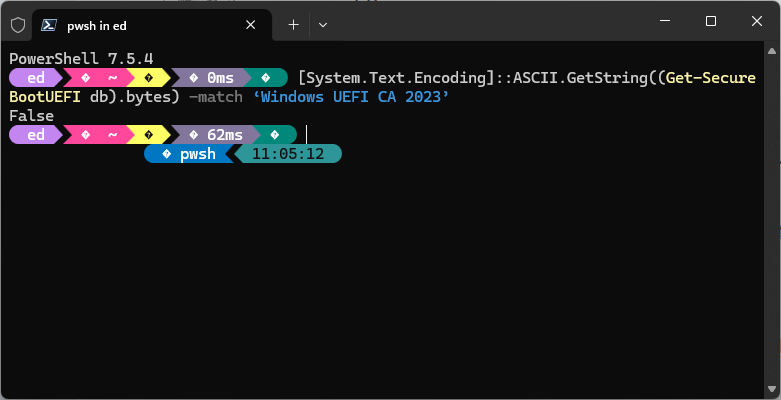
Here in Windows-World, you can make big changes without incurring at least some risk. This morning, I wondered if I’d bitten off more than I could chew. I even wondered if I’d bricked the Flo6. Thank goodness, I had not. I’ll take that as a win, even though you can see in the lead-in graphic that 2023 keys remain absent on this PC. Go figure!


Facebooklinkedin
Facebooklinkedin

Understanding El-Cheapo Windows Licenses

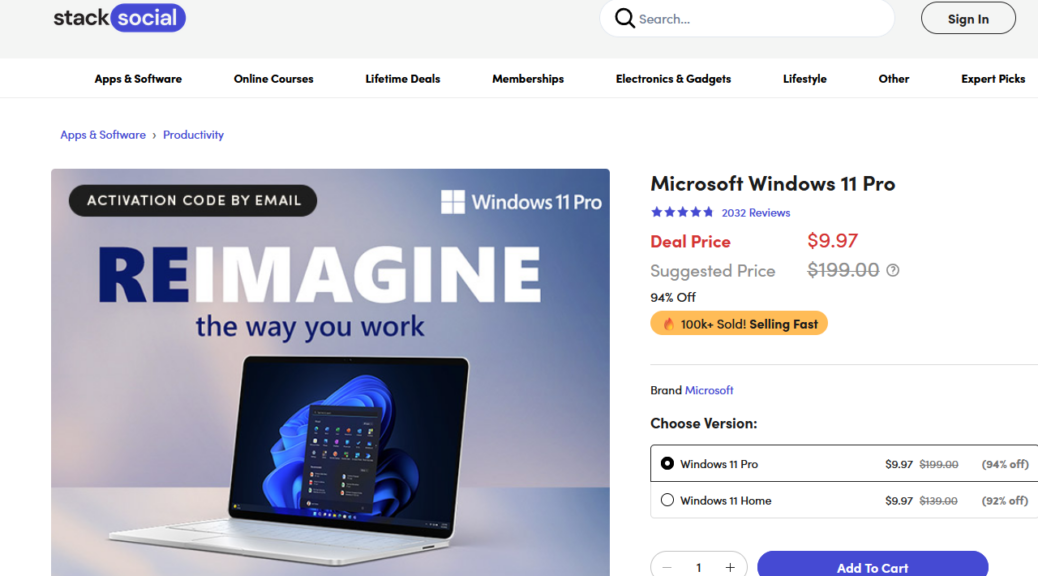
Every so often, a new round of bargain‑basement Windows license deals makes the rounds. You’ve seen them: Windows 11 Pro for ten bucks, Windows 10 Pro for even less. They pop up on StackSocial, StackCommerce, and a handful of deal‑driven tech sites. And like clockwork, the obvious question arises: Is this for real, or too good to be true? Neither and both: indeed, understanding el-cheapo Windows licenses hits both sides of this common wisdom.

More On Understanding El-Cheapo Windows Licenses

As someone who’s been around the Microsoft ecosystem for a long time — and who has more legit keys than I’ll ever need thanks to MVP status — I find the whole phenom fascinating. Not because I need another license, but because these offers sit right at the intersection of Microsoft’s licensing rules, its activation infrastructure, and the gray‑market economy surrounding both.

Here’s the key (pun intended): activation and licensing are not the same. Activation is a technical handshake with Microsoft’s servers. Licensing is a legal framework that governs how a key is properly obtained and used. Those two systems overlap, but they don’t enforce each other as tightly as many expect and assume.

Most $10 keys fall into one of three buckets. The first is unused OEM keys pulled from bulk hardware purchases. Perfectly valid keys, never activated on their original devices, but not transferable under Microsoft’s rules. The second bucket is decommissioned or oversold MAKs (multiple activation keys) — volume license keys with high activation counts that get resold repeately. They activate until the pool runs dry. The third bucket is region‑restricted retail keys, bought cheaply in low‑cost markets and resold elsewhere. They activate just fine, and Microsoft rarely retroactively enforces region boundaries.

None of these keys is counterfeit. They’re simply not authorized for retail distribution and sales. And that’s the crux of the matter. A key can be technically valid and still not legitimate under Microsoft’s licensing terms. That’s why you see disclaimers like “Microsoft may deactivate this license” — something never attached to a true retail key.

Why Not Stop This Madness?

So why doesn’t Microsoft shut this down? Because enforcement is aimed at organizations, not individuals.  Say a corporate MAK pool gets audited and is found to be leaking keys. Then, the consequences fall on the organization that holds the license — not the end user who bought a $10 key online. Microsoft’s activation infrastructure is built for compatibility and ease of deployment, not aggressive policing. As long as the upstream license pool stays quiet, the key will likely keep working.

That’s why you see technically savvy users reporting years of trouble‑free activation. They’re not wrong. They’re simply describing the operational reality, not the licensing reality.

In the end, these cheap keys occupy a curious middle ground: not fake, not fully legitimate, but functional and low‑risk for individual buyers. They’re a reminder that Windows licensing is strict on paper, pragmatic in practice, and full of gray areas that only get more interesting the deeper you dig.

Here in Windows-World one perforce gets comfortable with gray areas. This one seems a bit more gray and shadowy than most, but there you have it!

Facebooklinkedin
Facebooklinkedin